

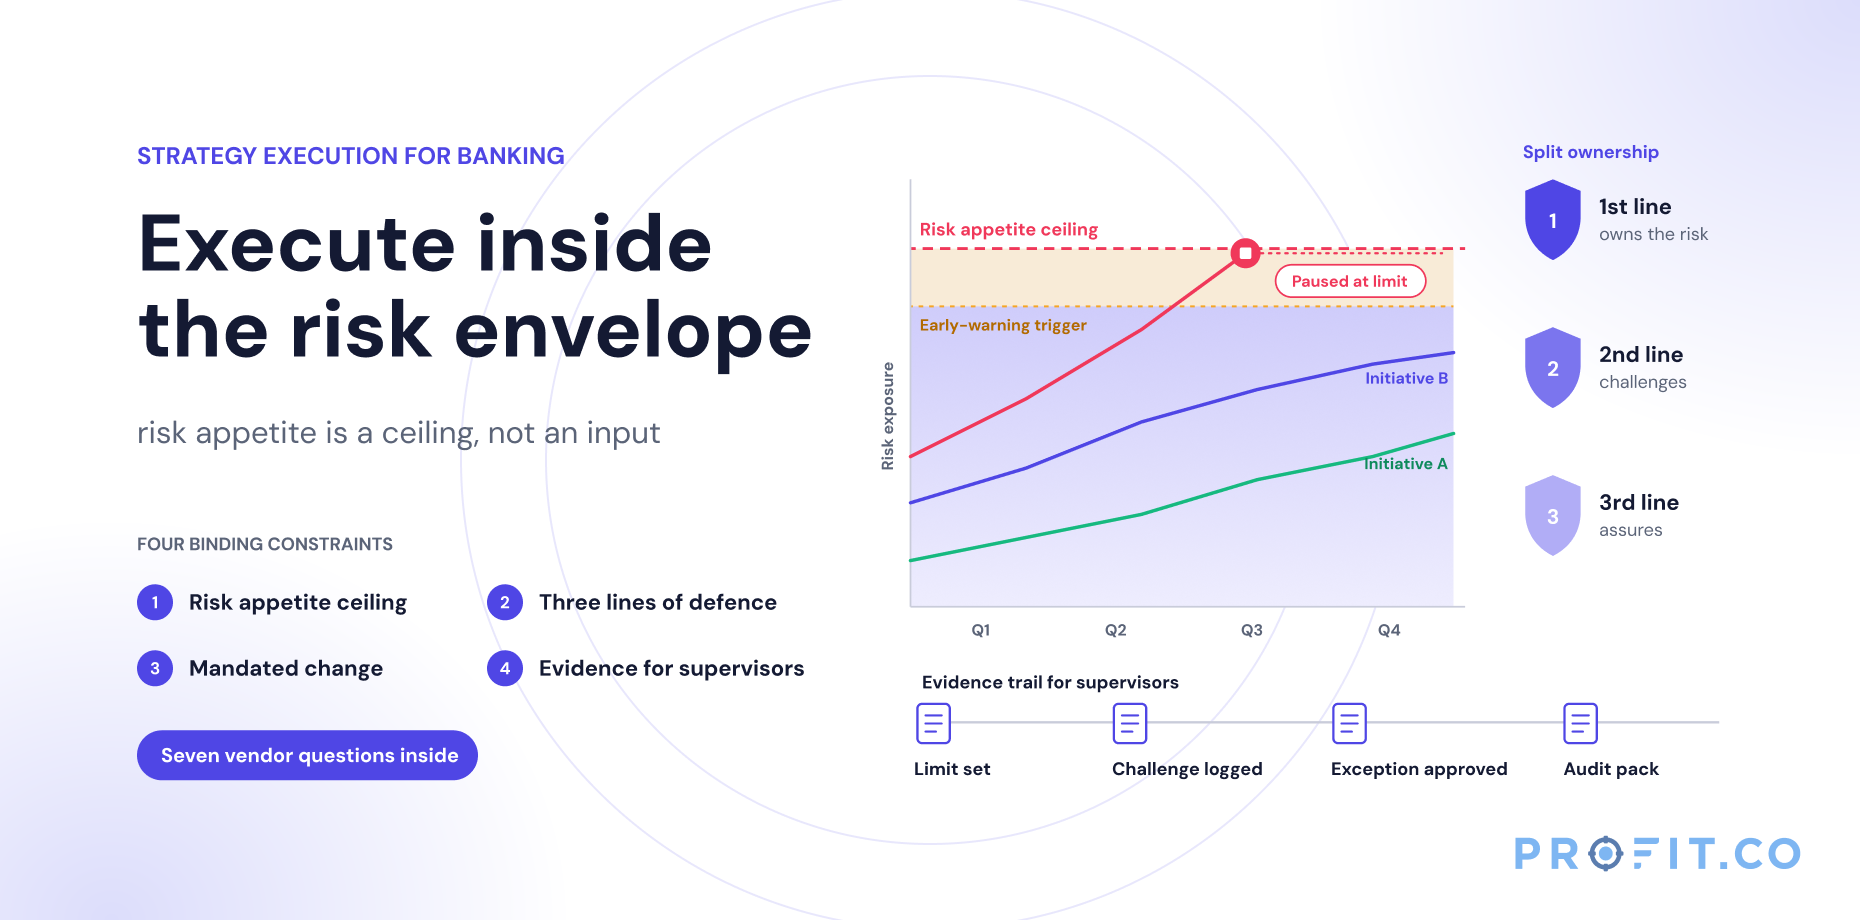
In most sectors risk is something strategy considers. In banking it is a ceiling set before strategy starts, by people who do not report to whoever owns the plan.
Strategy execution software for banking has to operate inside constraints most platforms treat as reporting categories. Four define the sector: risk appetite functions as a binding ceiling on growth objectives rather than a consideration; the three-lines-of-defence model splits ownership of a single objective across business, risk, and audit functions that do not report to each other; a large share of the change portfolio is regulatory and arrives on external timelines; and every material decision must be evidenced to supervisors and internal audit years later. A platform that cannot express a limit, hold split ownership, schedule mandated work to real dates, and produce an immutable decision record will generate objectives the second line has to block after they have been committed.
Table of Contents
In this article
- Banking’s Difference: Strategy Has a Ceiling
- Why Generic Platforms Encode the Wrong Model
- Constraint 1, Risk Appetite as a Binding Limit
- Constraint 2, Three Lines of Defence Splits Ownership
- Constraint 3, Mandated Change You Did Not Choose
- The Four Constraints and What Each Requires
- Constraint 4, Everything Must Be Evidenced
- Banking KPIs Across the Envelope
- Framework Fit for a Bank
- Three Banking Deployments
- Questions to Ask a Vendor
- Seven Mistakes in Banking Strategy Deployments
- A Rollout Sequence for a Bank
- Frequently Asked Questions
Key Takeaways
- Risk appetite is a ceiling, not an input: growth objectives in banking are bounded before they are set, and a platform that cannot express a limit alongside a target will produce commitments the second line has to unwind.
- Ownership of one objective is genuinely split: under three lines of defence, the business owns delivery, risk and compliance own challenge, and internal audit owns assurance, across functions that do not report to each other.
- Much of the change portfolio is not chosen: regulatory and supervisory work arrives on external timelines, and mixing it with discretionary strategy in one undifferentiated backlog guarantees the discretionary work loses.
- Evidence is a first-class requirement: decisions must be reconstructable years later for supervisors and internal audit, which makes an immutable activity log a functional requirement rather than a nice-to-have.
- Control-type measures matter more here than elsewhere: many banking measures must stay within a band rather than move in one direction, and Profit.co’s own banking guidance uses increase, control, and milestone KPI types side by side.
- Ask about audit trails before features: full audit trails, role-based access, and evidence export determine whether the platform survives an internal audit review, and that review will happen.
1. Banking’s Difference: Strategy Has a Ceiling
Strategy execution in most industries is an optimization problem: given finite resources, choose the highest-value priorities and pursue them. Banking adds a constraint that changes the shape of the problem entirely. Whatever the strategy proposes, it must fit inside a risk envelope the board has approved and a supervisor scrutinizes.
That envelope is not advisory. A growth objective that would take the bank outside its stated appetite is not an ambitious target; it is a target the second line is obliged to challenge and, if committed anyway, a finding waiting to be raised. The constraint binds before the strategy is written, and it is enforced by people who do not report to whoever owns the plan.
What this changes about the software requirement
- A target alone is insufficient. Every growth objective needs a companion limit, visible in the same view, so the ceiling is present at the moment of commitment rather than raised afterwards.
- Objectives have more than one owner. The business owns delivery, risk and compliance own challenge. A platform with a single owner field cannot express this without distorting it.
- Much of the portfolio is not optional. Regulatory change consumes a substantial share of capacity on dates nobody internal chose.
- The record outlives the cycle. A decision made this quarter may be examined in three years by a party who was not present.
None of this makes banking harder to serve than other sectors. It makes it different, in ways that a generic configuration will get wrong in specific, predictable places. Profit.co maintains a dedicated set of banking material covering loan operations, trade operations, treasury, and advisory services in its banking industry insights, and the examples throughout this article draw on it.
2. Why Generic Platforms Encode the Wrong Model
Most strategy platforms are built around three assumptions that hold almost everywhere and fail in a bank.
Assumption 1: more is better
Goal systems are designed around improvement in one direction. Increase revenue, reduce cost, raise satisfaction. A significant share of banking measures do not behave that way, they must stay inside a range, and moving too far in the favourable direction is itself a signal. A platform that can only express “higher is better” forces those measures into a shape that misrepresents them.
Assumption 2: one objective, one owner
Single ownership is sound advice in most organizations and incomplete in a regulated bank, where accountability is deliberately distributed across lines of defence. Forcing a single owner field produces either a business owner with no visible challenge function or a risk owner who appears accountable for commercial delivery.
Assumption 3: the record is for us
Most organizations keep a decision record for internal continuity. A bank keeps it because a supervisor or internal audit may reconstruct the decision later, and the standard of evidence is higher, who decided, on what basis, what alternatives were considered, and when.
The consequence of these three is a deployment that looks successful for two quarters and then collides with the second line. The pattern is not unique to banking in form, it is the same structural drift Profit.co describes in why most companies get strategy and operations alignment wrong, but the consequences here are supervisory rather than commercial.
3. Constraint 1, Risk Appetite as a Binding Limit
The requirement: express a ceiling alongside a target, in the same view, at the moment of commitment.
A commercial objective to grow lending in a segment is incomplete without the appetite limits it operates within, concentration, credit quality, capital consumption. In practice those limits usually live in a risk system while the growth objective lives in the strategy platform, and they meet in a committee paper once a quarter.
How to express a limit in a goal system
This is exactly what control-type measurement is for. Where an increase KPI drives a number upward and a decrease KPI drives it down, a control KPI holds a value inside a band, and Profit.co supports four progress calculation methods for the Control KPI type, because “on target” for a control measure is a range rather than a threshold. Profit.co’s own banking guidance already uses the types side by side: in its treasury and cash management example, one key result uses an increase KPI, a second uses a control KPI, and a third uses a milestone KPI within the same objective. The worked example is in improving treasury and cash management.
Pairing growth with its constraint
- Every growth objective carries at least one control key result. The commercial target and the boundary condition sit in the same objective rather than in two systems.
- Threshold alerts fire on the limit, not the target. Profit.co supports configurable threshold alerts on projects, portfolios, tasks and milestones with conditions combining by AND within a group and AND or OR across groups, firing through the Action Center, email, a dashboard badge, or a webhook. A compound trigger, growth ahead of plan while a control measure approaches its band edge, is one alert rather than two unrelated ones.
- The limit is visible to the business, not only to risk. A ceiling nobody in the first line can see is a ceiling they will hit.
4. Constraint 2, Three Lines of Defence Splits Ownership
The requirement: hold delivery accountability and challenge accountability on the same objective without collapsing them.
The three-lines model is standard governance across financial services: the business owns and manages risk in the first line, risk and compliance functions provide oversight and challenge in the second, and internal audit provides independent assurance in the third. It exists precisely so that no single function both performs and validates its own work.
Strategy platforms rarely model this. The usual result is that the first line owns everything in the system and the second line operates outside it, reviewing in committee papers rather than in the same record. Challenge then happens late, in a forum, rather than continuously in the working system.
What the platform needs
- Role-scoped visibility rather than uniform access. Profit.co supports per-role widget access with financial and executive content gated behind explicit permissions, and widgets a role cannot access hidden rather than shown inactive.
- Governance items distinct from goals. Challenge, escalation, and open questions need somewhere to live that is not a comment on a key result. Profit.co’s Governance module provides eight independently configurable categories, Actions, Assumptions, Decisions, Issues, Risks, Strategic Alignment, Project Changes, and Tollgates, each with its own status lifecycle and owner, which lets a second-line challenge be a tracked object rather than a meeting note.
- Risk-to-issue escalation as a recorded path. A risk that materialises can be escalated to an Issue, with both records cross-linked and the escalation captured on each activity log. That linkage is what an auditor follows.
- Assumptions tracked explicitly. The Assumptions category covers factors believed true for planning that still require validation. In a bank, unvalidated assumptions underneath a growth plan are second-line territory and should be visible as objects rather than buried in narrative.
5. Constraint 3, Mandated Change You Did Not Choose
The requirement: separate mandated work from discretionary strategy, and schedule it to real dates.
A meaningful share of a bank’s change capacity goes to work nobody chose: regulatory implementation, supervisory remediation, reporting obligations. These arrive with external deadlines and no option to descope.
Entering them as ordinary objectives on a quarterly cycle creates a predictable failure. Mandated work competes with discretionary strategy for attention and wins late, consuming everything as a deadline approaches, while the strategic agenda quietly slips. Nothing in an undifferentiated backlog shows leadership that collision coming.
What the platform needs
- Classification that distinguishes mandate from choice. Not because mandated work matters less, but because it is managed differently: a discretionary objective can be re-scoped, a regulatory one cannot.
- Fixed-date scheduling. Profit.co supports scheduling by exact datetime as an alternative to interval-based cycles, so a regulatory deadline holds its real date rather than the nearest quarter boundary.
- Stage gates for multi-phase programmes. Tollgate-based progress reporting with weighted gates and mandatory approval before advancement matches how remediation programmes actually progress better than a completion percentage does.
- Capacity visibility across both portfolios. The question leadership needs answered at planning time is how much discretionary capacity remains after mandated work is funded, which requires both to sit in one portfolio view.
6. The Four Constraints and What Each Requires
An evaluation grid. The final column is answerable in a demo, and each question separates a platform that can operate in a regulated environment from one that will need workarounds.
| Constraint | Why Generic Platforms Struggle | What It Requires | Question to Ask a Vendor |
|---|---|---|---|
| 1. Risk appetite as a ceiling | Goal systems assume more is better in one direction | Control-type KPIs with bands; compound threshold alerts; limits visible to the first line | “Show me a growth objective with its appetite limit in the same view.” |
| 2. Three lines of defence | One objective, one owner is the default model | Role-scoped access; governance objects separate from goals; recorded escalation paths | “How does a second-line challenge get recorded against this objective?” |
| 3. Mandated change | All work treated as chosen and cycle-relative | Mandate classification; fixed-date scheduling; stage gates; joint capacity view | “How do I schedule a regulatory deadline to its real date?” |
| 4. Evidence for supervisors | Decision history assumed to be for internal continuity | Immutable activity logs; who decided and why; exportable evidence | “Reconstruct for me who changed this item, when, and on what basis.” |
The second question is the one most platforms answer badly, because it exposes whether governance is a first-class object in the system or a comment field attached to a goal. Sector-general evaluation criteria that still apply here are set out in how to choose the right strategy execution platform.
See growth objectives and their limits in one view
7. Constraint 4, Everything Must Be Evidenced
The requirement: a decision made today must be reconstructable years from now by someone who was not present.
Internal audit will review the strategy process. Supervisors may ask how a particular commitment was arrived at. In both cases the question is not what the outcome was but how the decision was made, what was known, what was considered, who approved it, and when.
What satisfies that standard
- Automatic capture, not manual minuting. Profit.co records every change to a governance item automatically with the acting user and a timestamp, giving an audit record with no additional logging step. Evidence that depends on someone remembering to write it down is evidence that will have gaps.
- Decisions as a tracked object type. The Decisions category records what was chosen, what alternatives were considered, and the rationale. That triplet is close to exactly what an audit reviewer asks for.
- Immutability. A log that can be edited after the fact is not an audit trail. Profit.co describes its governance activity logs as immutable.
- Documented security posture. Profit.co publishes SOC 2 Type II, ISO 27001, GDPR compliance, and a 99.9% uptime SLA on its strategic planning software page, alongside role-based access controls and full audit trails. For a bank’s third-party risk assessment these are table stakes rather than differentiators, but their absence ends an evaluation.
A note on scope
This article addresses strategy execution tooling, not regulatory compliance systems. Capital calculation, regulatory reporting, and risk measurement belong in dedicated systems, and a strategy platform should consume outputs from them rather than attempt to replace them. Nothing here is legal or regulatory advice, and requirements vary materially by jurisdiction and institution type, your second line and compliance function should define the standard the platform must meet.
8. Banking KPIs Across the Envelope
Measures drawn from Profit.co’s banking guidance, with the KPI type each naturally takes. Movements shown are the illustrative figures in Profit.co’s own examples rather than benchmarks or targets.
| Domain | Measure | KPI Type | Illustrative Movement |
|---|---|---|---|
| Branch operations | Transactions processed per teller hour | Control | Maintain an average of 10 |
| Branch operations | Retail branch lobby wait time | Control | No more than 5 minutes |
| Cost efficiency | Cost per teller transaction | Decrease | $4 to $1 per transaction |
| Lending | Mortgage application processing time | Decrease | Two weeks to one week |
| Wealth management | New private banking accounts per employee | Increase | Up by 15% |
| Wealth management | Interested investors | Increase | 25 to 45 |
| Treasury | Mixed objective spanning three KPI types | Increase, Control, Milestone | One objective, three key result types |
The final row is the instructive one. Profit.co’s treasury example places an increase KPI, a control KPI, and a milestone KPI inside a single objective, growth, boundary, and delivery step together. That is the shape most banking objectives should take, and it is the shape a platform limited to increase-and-decrease measurement cannot produce. Branch and wealth figures come from ten banking OKR examples; the lending figure from improving loan operations.
9. Framework Fit for a Bank
Banks typically arrive with an existing performance framework, frequently a Balanced Scorecard maintained by finance or a strategy function, and a newer interest in OKRs from a transformation team. As in most regulated sectors, standardizing on one is usually the wrong instinct.
- Balanced Scorecard for the standing view. Profit.co’s Balanced Scorecard module holds Financial, Customer, Internal Process, and Learning and Growth perspectives in one live scorecard. For a bank the Internal Process perspective is where control effectiveness and operational resilience naturally sit, which keeps them visible alongside commercial performance rather than in a separate risk pack.
- OKRs for the change agenda. Discrete initiatives with a beginning and an end, a digital onboarding programme, a segment entry, a remediation. Profit.co’s banking material consistently shows business-unit OKRs aligning upward to corporate objectives such as improving profitability, which is the pattern that keeps a branch or treasury objective connected to the enterprise plan.
- Roadmaps for multi-year programmes. Core system replacement and multi-year regulatory programmes outlast quarterly cycles. Strategy roadmaps cascade vision areas into themes, sub-themes, and initiatives on a single timeline.
The practical test is the same one that works elsewhere: if a measure should never go away, it belongs on the scorecard; if it describes something you are changing this year, it belongs in an objective. What banking adds is a third question, if it is a boundary rather than a goal, it belongs in a control measure paired with whatever it bounds.
10. Three Banking Deployments
Three composite scenarios, each showing a different constraint handled badly and what would have caught it.
Deployment A, The growth objective with no ceiling
A commercial bank sets an ambitious objective to grow lending in a specific segment. Delivery is strong and the objective tracks green for two quarters. In the third, the second line raises a concentration concern; origination is curtailed mid-quarter, relationship managers who hit their targets are stood down, and the objective closes at roughly half its target.
What went wrong: Constraint 1. The growth target existed in the strategy platform; the concentration limit existed in the risk system. Neither was visible from the other, so nobody saw the trajectory approaching the boundary until it arrived. A control key result on concentration inside the same objective, with a threshold alert on the band edge rather than on the growth target, would have surfaced this in month four, while the response was still a re-plan rather than a stop.
Deployment B, Challenge that lived outside the system
A retail bank rolls out OKRs across business lines. Risk and compliance are given read-only access. Second-line challenge continues to happen in monthly committee papers. Six months later, internal audit observes that strategic objectives show no evidence of independent challenge, despite challenge having occurred throughout.
What went wrong: Constraint 2, compounded by Constraint 4. The challenge was real and the record of it was not in the system where the objectives lived, so from an evidentiary standpoint it had not happened. Recording second-line challenge as governance objects against the objective, with owner, status, and an automatic activity log, would have produced the evidence as a by-product of the work rather than as a retrospective exercise.
Deployment C, The quarter regulatory change consumed
A mid-sized bank plans a quarter with eight strategic objectives across business lines, alongside a regulatory implementation entered as one more objective on the same cycle. The implementation deadline falls six weeks in. Change capacity is redirected, six of the eight objectives stall, and the quarter is written off internally as a lost cycle.
What went wrong: Constraint 3. The collision was entirely predictable at planning time and invisible in the system, because mandated work sat in the same undifferentiated backlog as discretionary work on the same cadence. Classifying it as mandated, scheduling it to its real date with stage gates, and showing remaining discretionary capacity after it was funded would have led to a quarter with four objectives that were achieved rather than eight that were not.
The common thread: in all three the platform was capable and the configuration encoded an assumption that does not hold in a regulated bank. Each failure was visible in the data the organization already held, and none was visible in the view leadership was looking at.
11. Questions to Ask a Vendor
1. “Show me a growth objective with its limit in the same view.”
Tests whether the platform can express a boundary as a first-class measure rather than as commentary. Ask to see a control-type key result with a defined band alongside an increase target in one objective.
2. “How does second-line challenge get recorded against an objective?”
If the answer is a comment field, challenge will not survive audit review. Look for governance objects with their own owner, lifecycle, and automatic history.
3. “Reconstruct who changed this item, when, and on what basis.”
The audit trail question, asked as a demonstration rather than a feature claim. Ask specifically whether the log can be edited after the fact.
4. “How do I schedule work to a fixed regulatory date?”
Tests whether the platform assumes cycle-relative scheduling. A deadline that snaps to the nearest quarter is not a deadline.
5. “How granular is role-based access?”
In a bank this determines whether business-line performance detail is visible across lines, and whether second-line users see what they need without seeing what they should not.
6. “What do you provide for third-party risk assessment?”
Certifications, report dates and scope, hosting regions, and data handling. Ask for report dates rather than logos, an attestation covering a different period or product scope is weaker than it appears.
7. “What happens to the record when a user leaves?”
Decision history must survive personnel change. Ownership reassignment should not erase who made a decision at the time.
12. Seven Mistakes in Banking Strategy Deployments
1. Setting growth targets without their limits
The Deployment A failure. Every growth objective should carry at least one control measure representing the boundary it operates within.
2. Giving the second line read-only access and calling it involvement
Challenge that happens outside the system leaves no evidence inside it, which is the same as not having happened when audit reviews the process.
3. Treating every measure as increase-or-decrease
Many banking measures, wait times, throughput per head, utilisation, concentration, are control measures. Forcing them into a directional shape drives behaviour the strategy did not intend.
4. Mixing mandated and discretionary work in one backlog
Guarantees that discretionary strategy loses late and unpredictably, and removes the one signal that would have let leadership plan around it.
5. Relying on meeting minutes as the decision record
Minutes are written by someone, later, from memory. An automatic activity log capturing actor and timestamp is a different class of evidence.
6. Cascading enterprise financial measures to branch or desk level
A branch cannot move an enterprise profitability ratio within a quarter. Profit.co’s banking material consistently shows the opposite pattern, operational objectives at the unit level aligned upward to a corporate objective such as improving profitability, which is what keeps the connection real. The advisory services example follows exactly this structure in how OKRs help banks grow advisory and investment services.
7. Expecting the platform to be the compliance system
Strategy execution tooling consumes outputs from risk and regulatory systems. It does not replace them, and a deployment scoped as though it might will fail a second-line review.
13. A Rollout Sequence for a Bank
Phase 1, Bring the second line in before configuration
- Involve risk, compliance, and internal audit in the design rather than the review. A platform configured without them will be reconfigured after them.
- Agree how second-line challenge will be recorded, as governance objects with owners and lifecycles, not as comments.
- Confirm the third-party risk assessment requirements early; certifications, hosting, and data handling determine whether the evaluation proceeds at all.
Phase 2, Encode the envelope, not just the plan
- For each growth objective, identify the boundary conditions it operates within and express them as control key results in the same objective.
- Set threshold alerts on limits as well as targets, using compound conditions where a boundary matters only in combination, threshold alert configuration supports AND within a group and AND or OR across groups.
- Route limit alerts to the second line as well as the business owner.
Phase 3, Separate the two portfolios
- Classify mandated work distinctly and schedule it to real dates with stage gates.
- Produce a single capacity view showing discretionary capacity remaining after mandated work is funded, and plan the discretionary agenda against that number rather than against ambition.
Phase 4, Pilot on one business line with full vertical depth
- Choose a line with both growth objectives and control obligations, so the envelope is tested rather than deferred.
- Connect measures that already exist in source systems so values arrive rather than being entered, Profit.co syncs through its integrations catalogue with bi-directional updates.
- Run one full cycle including a review that produces recorded decisions, then have internal audit walk the record before extending. Portfolio-side framing sits on Profit.co’s page for PMO leaders, with the corporate view on its hub for strategy and transformation leaders.
Profit.co reports most customers complete setup and run their first cycle within two to four weeks, with enterprise rollouts involving custom integrations typically taking four to eight weeks alongside dedicated onboarding. For a bank, expect the upper end or beyond, the pacing constraint is almost always third-party risk assessment and second-line design involvement rather than platform configuration.
Run growth, limits, and mandated change in one portfolio
Frequently Asked Questions
A platform that connects a bank’s strategy to execution while operating inside the constraints the sector imposes: risk appetite as a binding ceiling on growth objectives, ownership split across three lines of defence, a change portfolio partly composed of mandated regulatory work on external deadlines, and an evidentiary standard requiring decisions to be reconstructable years later for supervisors and internal audit.
In most industries risk is something strategy considers. In banking it is a ceiling set before strategy starts and enforced by functions that do not report to the strategy owner. That changes the software requirement: every growth objective needs a companion limit visible in the same view, and a platform that can only express improvement in one direction will misrepresent a large share of banking measures.
Through control-type key results paired with the growth objectives they bound. Where an increase KPI drives a number up and a decrease KPI drives it down, a control KPI holds a value inside a band, and Profit.co provides four progress calculation methods for the Control type, because “on target” for a control measure is a range rather than a threshold. Threshold alerts should fire on the limit as well as the target.
It means a single objective genuinely has more than one accountable party, the business owns delivery, risk and compliance own challenge, internal audit owns assurance. Platforms with a single owner field cannot express this without distorting it. The workable approach is to record second-line challenge as governance objects against the objective, each with its own owner, status lifecycle, and automatic activity log.
Classify it distinctly and schedule it to real dates rather than cycle boundaries, since regulatory deadlines do not move to fit a quarterly cadence. Multi-phase programmes suit tollgate-based progress with weighted gates and approval before advancement. Most importantly, produce a capacity view showing what discretionary capacity remains after mandated work is funded, and plan the strategic agenda against that figure.
Automatic capture rather than manual minuting, recording the acting user and timestamp on every change; decisions as a tracked object type holding what was chosen, what alternatives were considered, and the rationale; immutability, since a log that can be edited afterwards is not an audit trail; and record survival through personnel change, so ownership reassignment does not erase who decided what at the time.
Yes, and it is usually the right structure. The scorecard suits standing measures across financial, customer, internal process, and learning perspectives, with control effectiveness and operational resilience sitting naturally in the internal process perspective. OKRs suit the change agenda. Multi-year programmes such as core system replacement suit a roadmap. Running them in one platform prevents the risk pack and the strategy plan becoming two accounts of the same year.
No. Capital calculation, regulatory reporting, and risk measurement belong in dedicated systems. A strategy platform should consume their outputs, typically as connector-fed KPIs, rather than attempt to replace them. A deployment scoped as though it might replace them will fail a second-line review, and should.


