Overview
Okta is a cloud-based identity management service that eliminates the burden of separate usernames and passwords across enterprise applications. It provides secure, centralized authentication and supports single sign-on (SSO), user lifecycle management, and automated provisioning across connected platforms.
The Okta SSO integration in Profit.co allows organizations to enable SAML-based single sign-on so employees can access Profit.co using their existing company credentials. SCIM-based user provisioning further automates user creation, updates, deactivation, and reactivation, keeping Profit.co accounts in sync with your Okta directory.
What This Integration Supports
With the Okta integration, you can:
- Enable SSO so users can access Profit.co using their existing Okta credentials
- Configure Okta as the SAML identity provider for Profit.co
- Push new users from Okta to Profit.co User Management automatically
- Push profile updates from Okta to Profit.co in real time
- Deactivate or reactivate Profit.co users based on Okta user status
- Import users from Profit.co to create new Okta users
Prerequisites
Before starting, ensure the following requirements are met:
- You have Okta administrator access
- You are logged in as a Super User or Admin in Profit.co
- The Profit.co app is available in the Okta App Catalog
- You have the API Key and SCIM Key from Profit.co Settings -> Security (required for user provisioning)
Note: Only Super Users can configure SSO and provisioning integrations in Profit.co.
For detailed instructions on creating and configuring a custom application in Okta for Single Sign-On (SSO) and SCIM user provisioning, refer to the App Creation Guide.
Configure Okta SSO for Profit.co
The following steps walk through setting up Okta as the SAML identity provider for Profit.co.
Step 1
Log in to your Okta account and navigate to the Admin panel.
- Open your browser and go to your Okta organization URL.
- Enter your Okta administrator credentials and sign in.
Step 2
Search for and add the official Profit.co application from the Okta App Catalog.
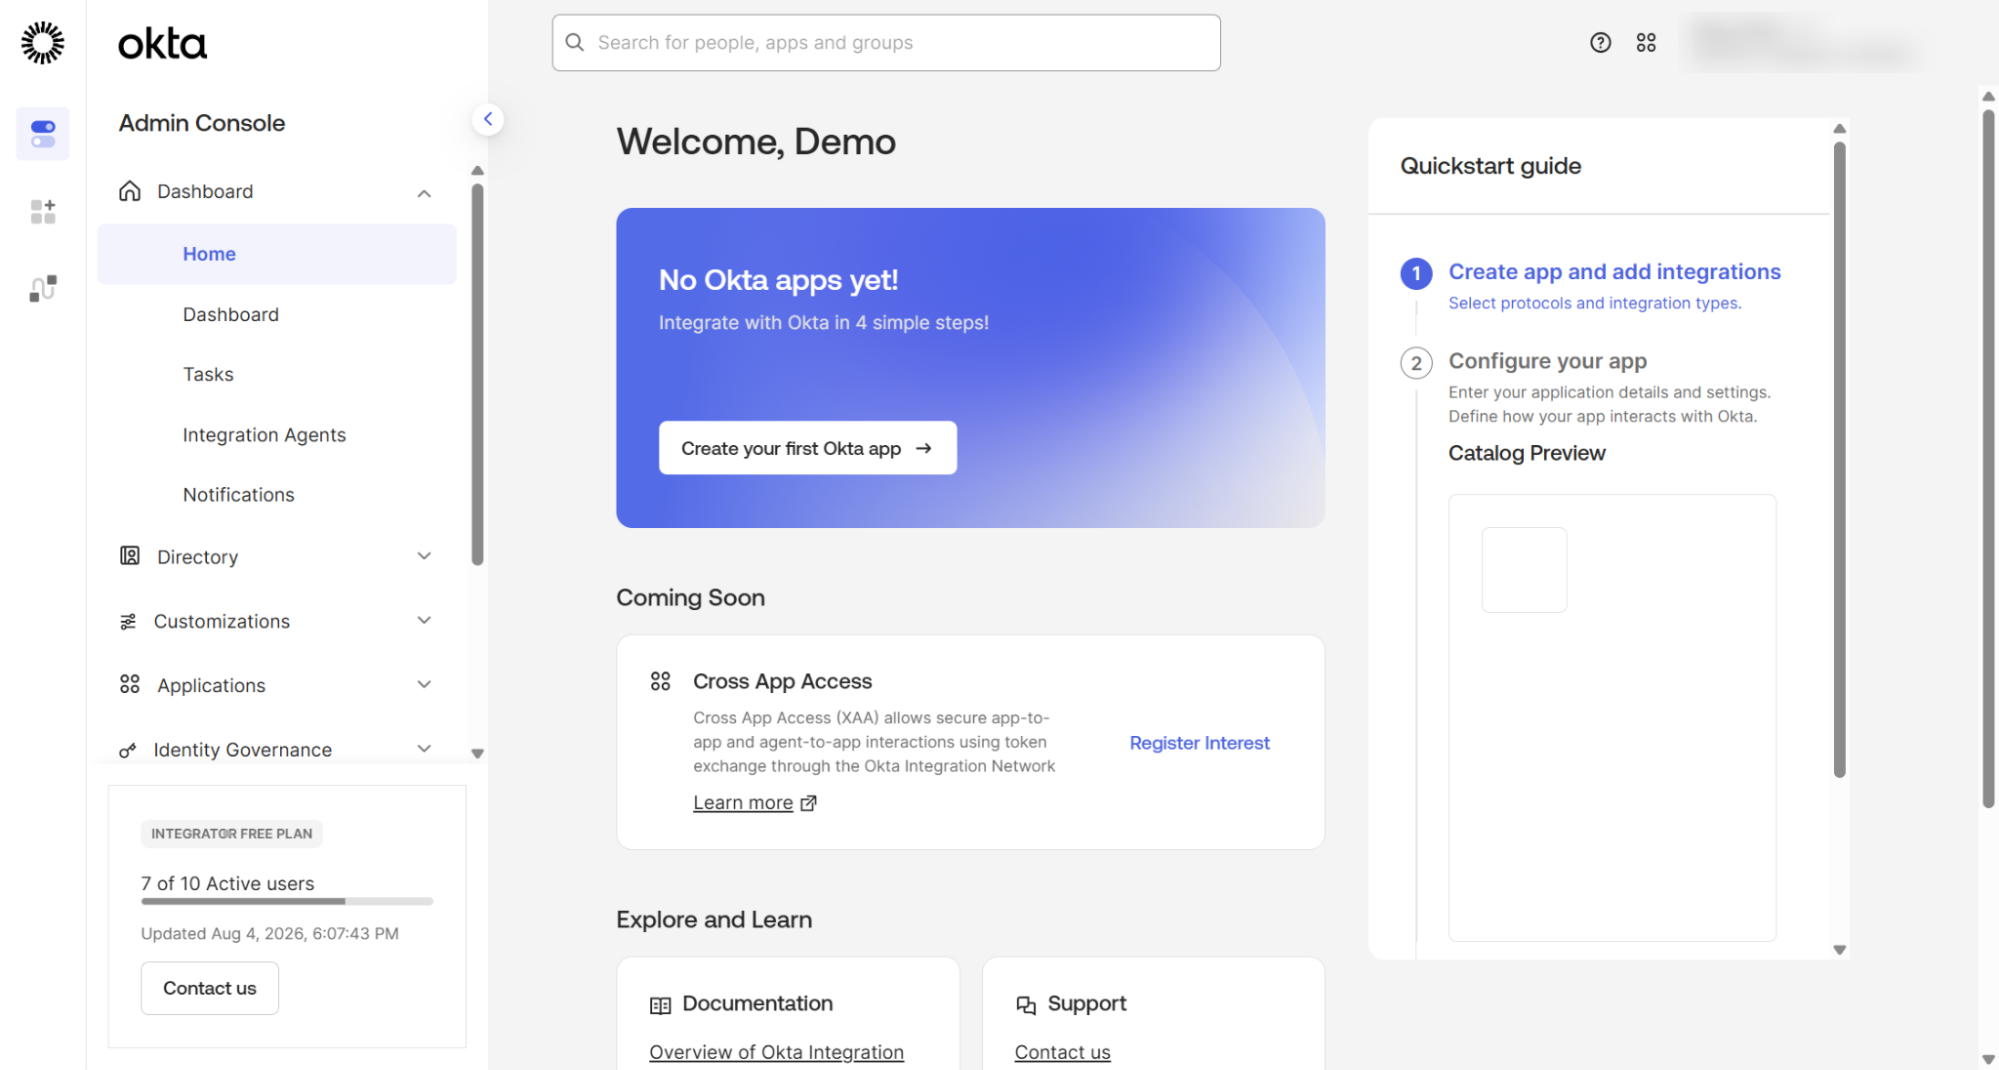
- From the Okta Admin dashboard, select Applications from the left navigation panel.
- Click Browse App Catalog to open the Okta integration catalog.
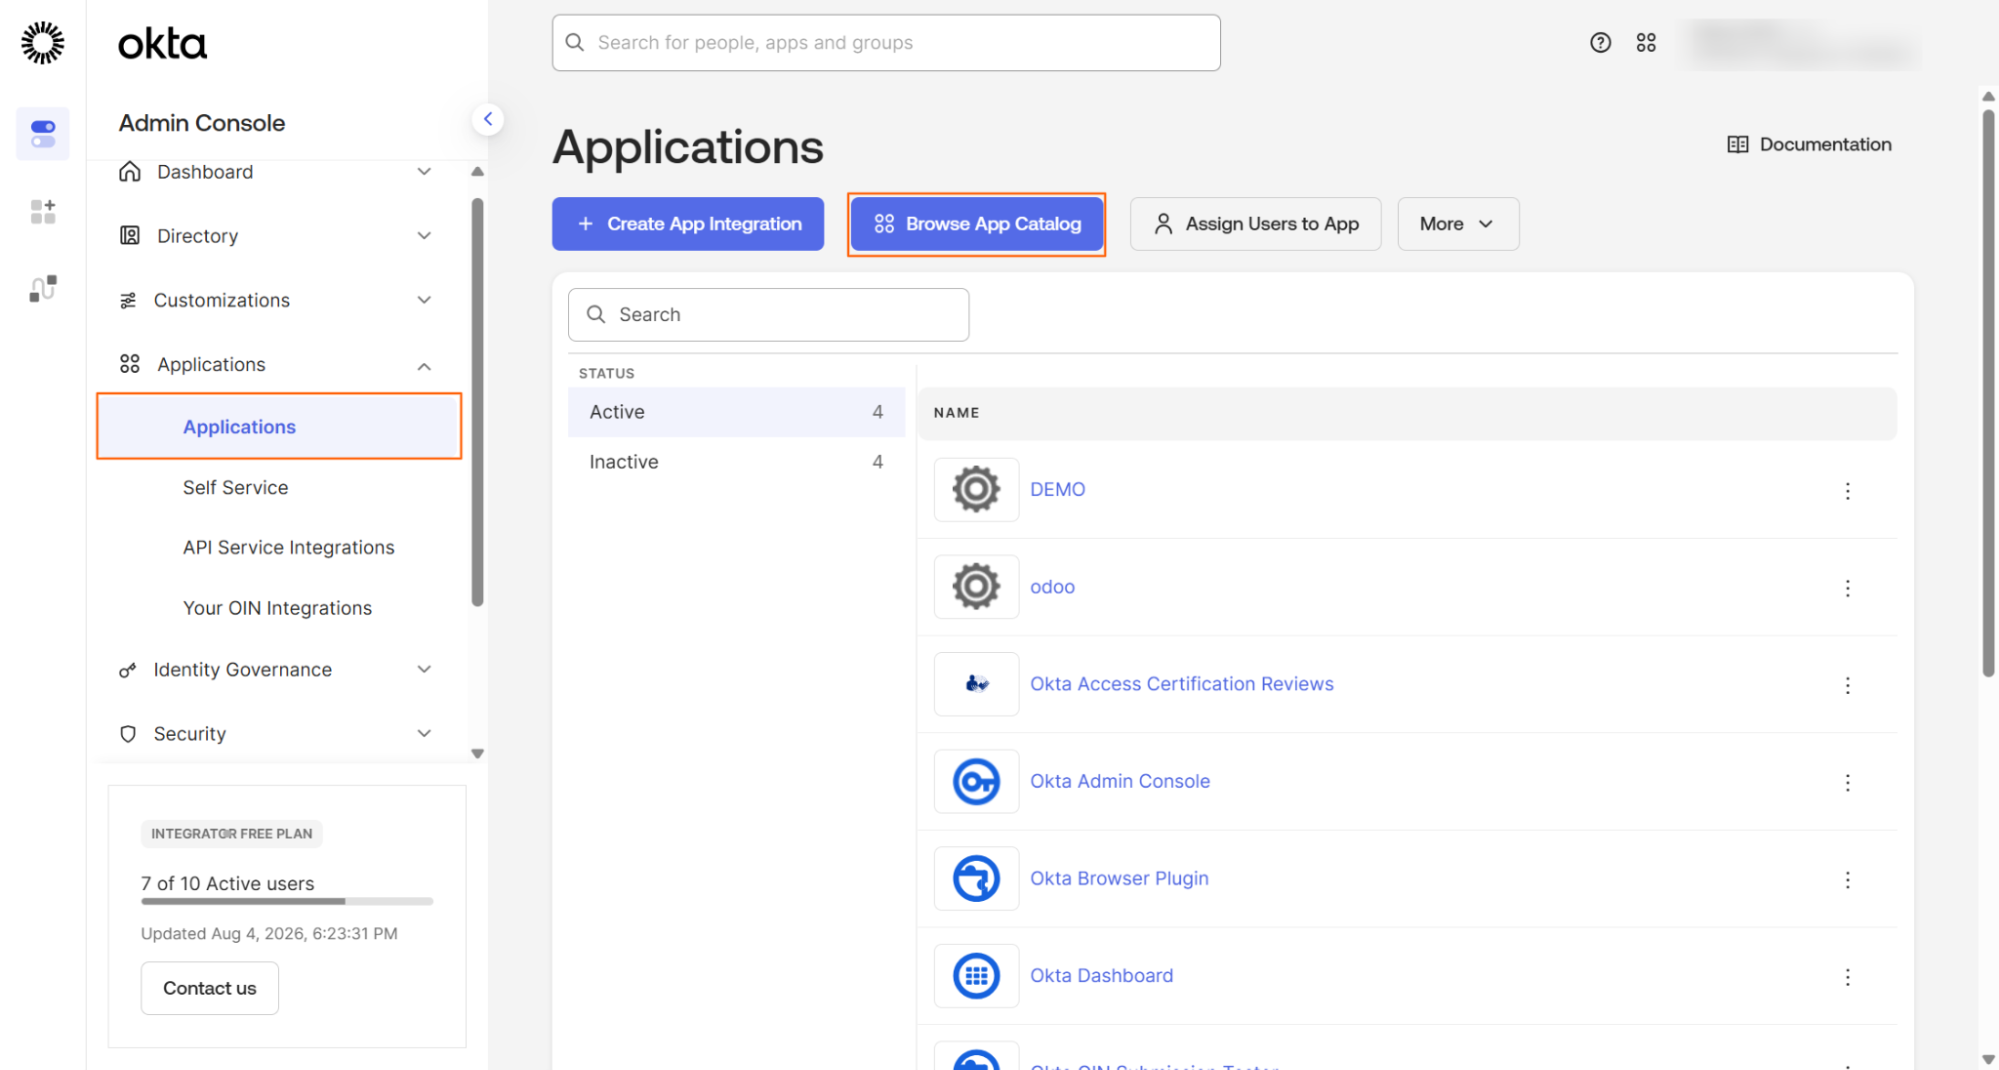
- In the search bar, type Profit.co and locate the official application.
- Click Add Integration to add the Profit.co app to your Okta account.
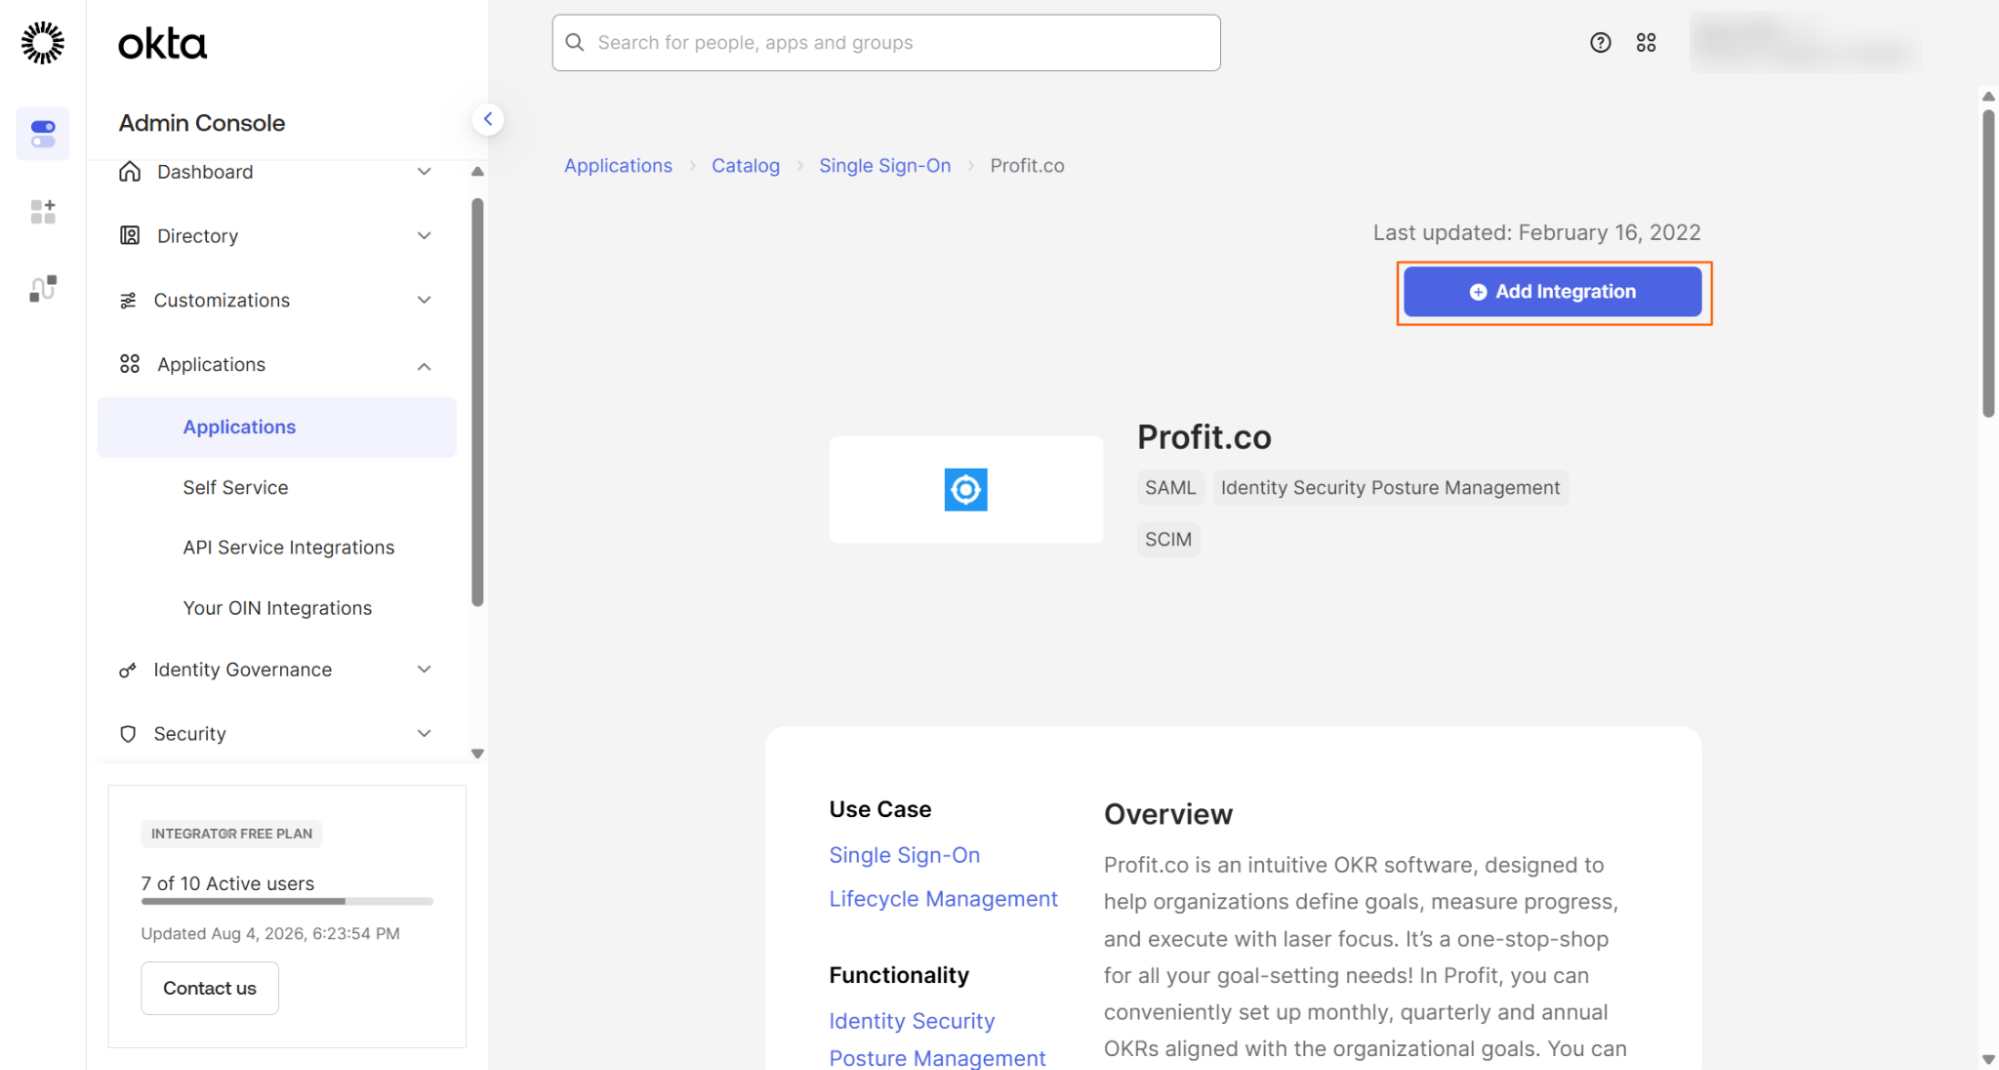
Note: Use the official Profit.co app from the Okta App Catalog to ensure full SAML and SCIM compatibility.
Step 3
Grant SSO access to Profit.co by assigning users or groups to the app.
- Click the Settings icon next to the Profit.co app.
- Select Assign to Users (or Assign to Groups) from the menu.
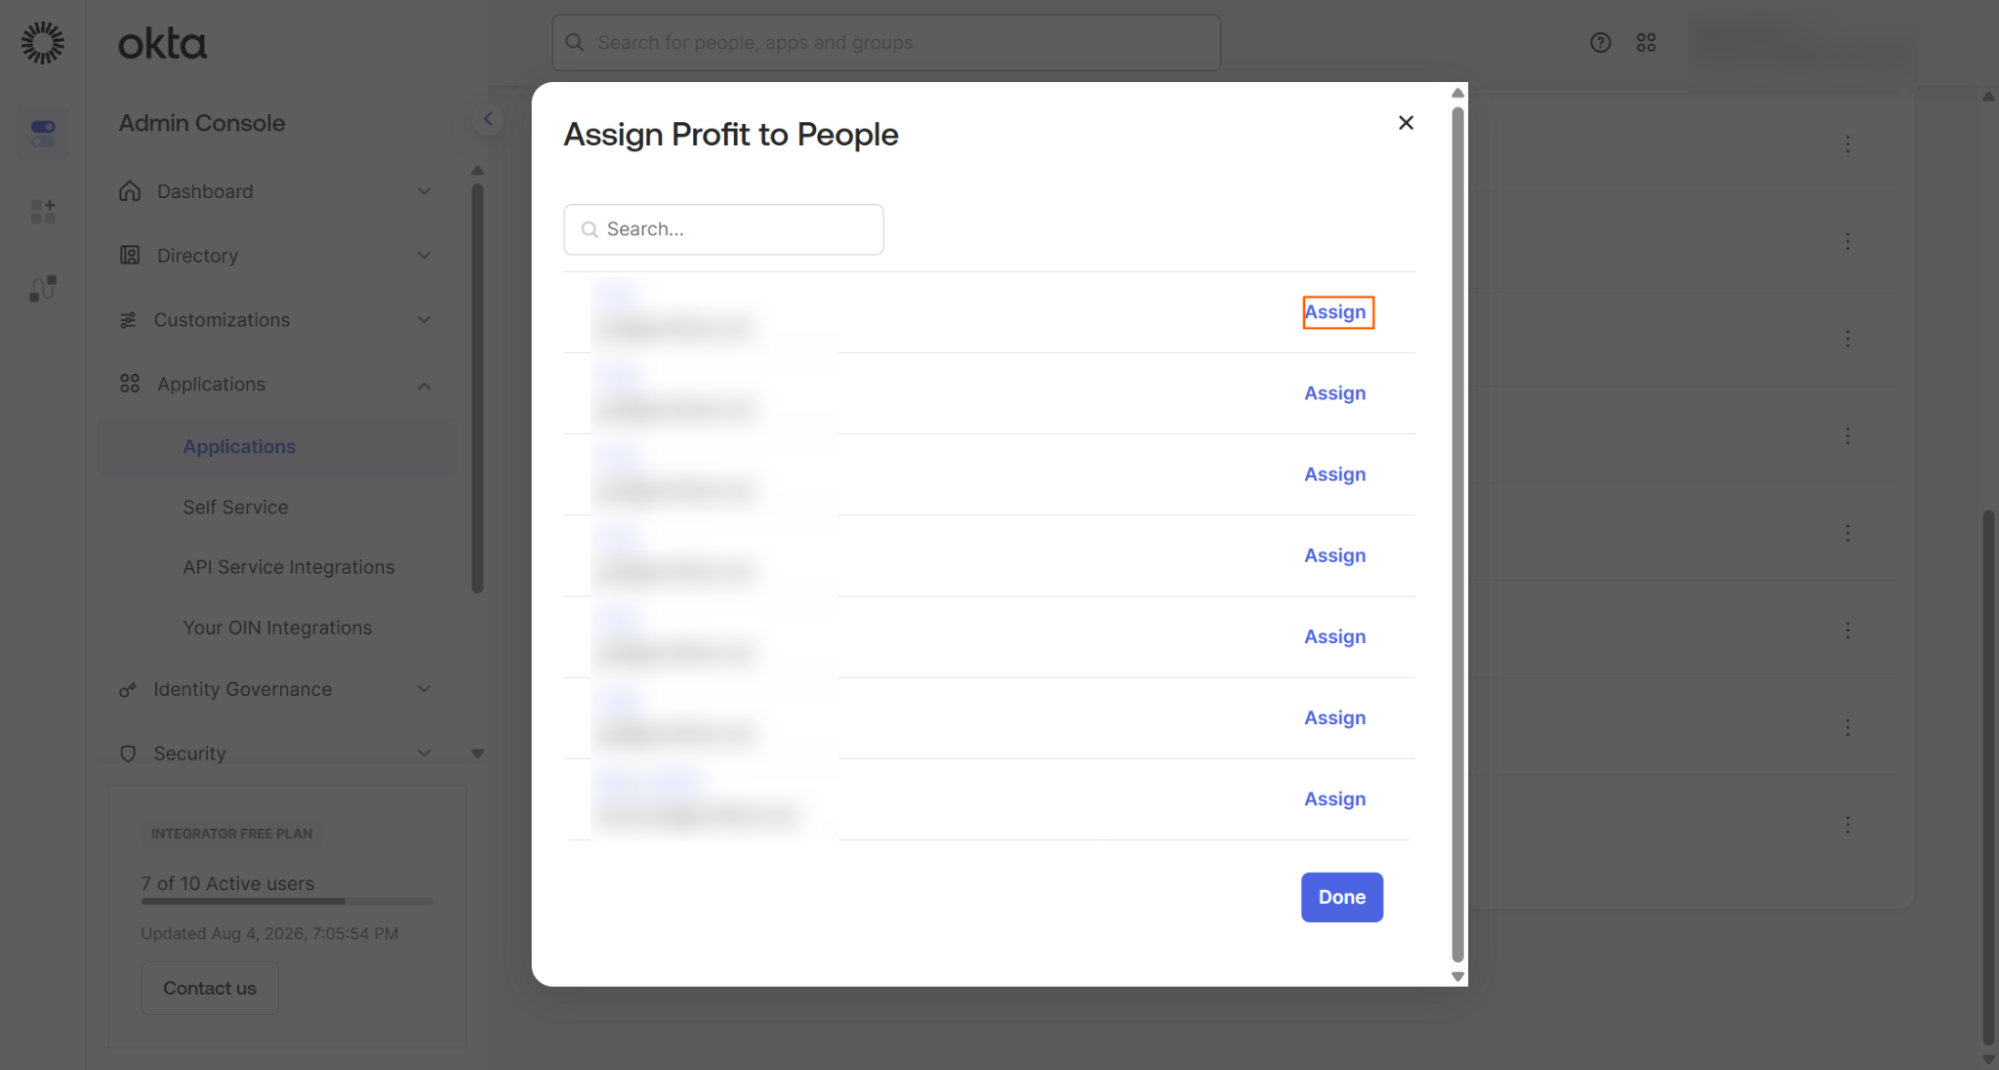
- Search for and assign the users or groups who should have SSO access to Profit.co.
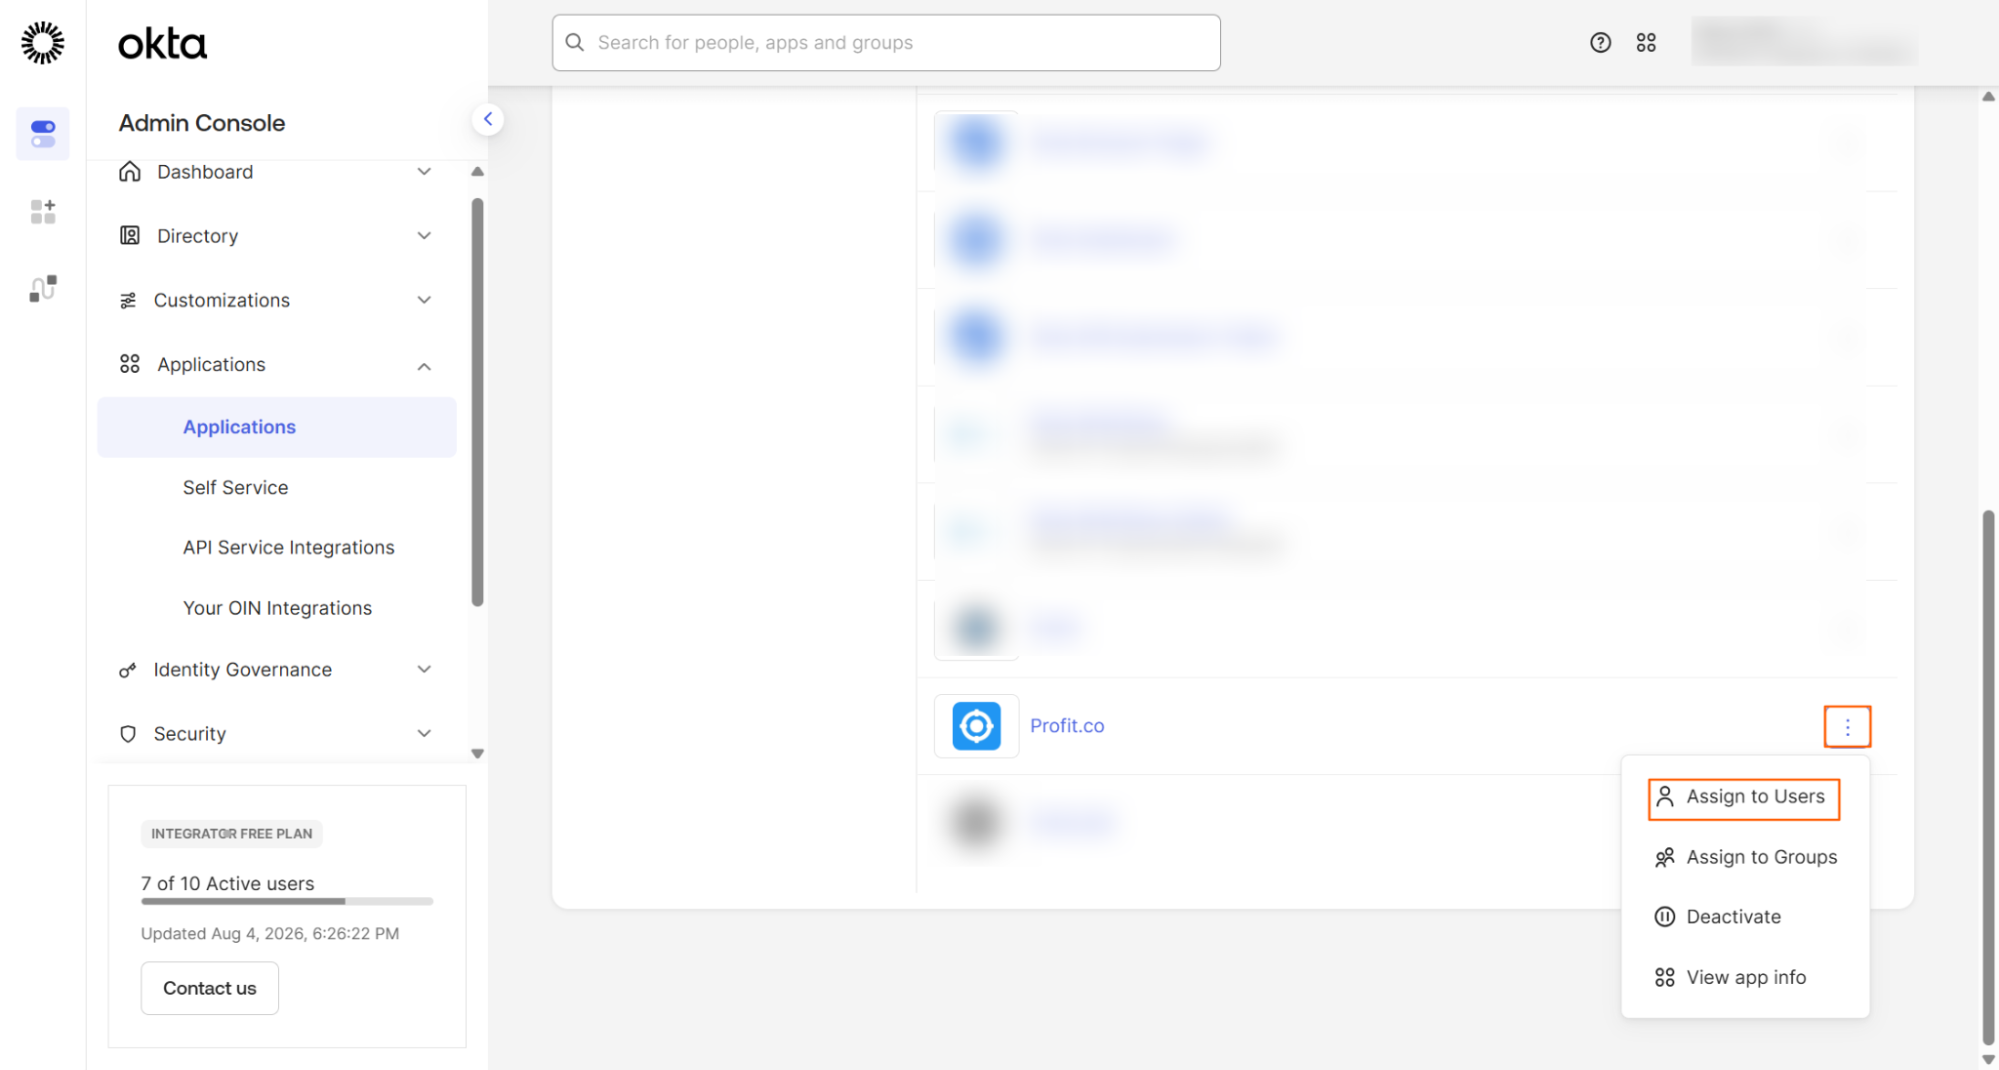
- Confirm each assignment — the status will show as Assigned once complete.
Step 4
- Click on the Profit.co app in your Applications list.
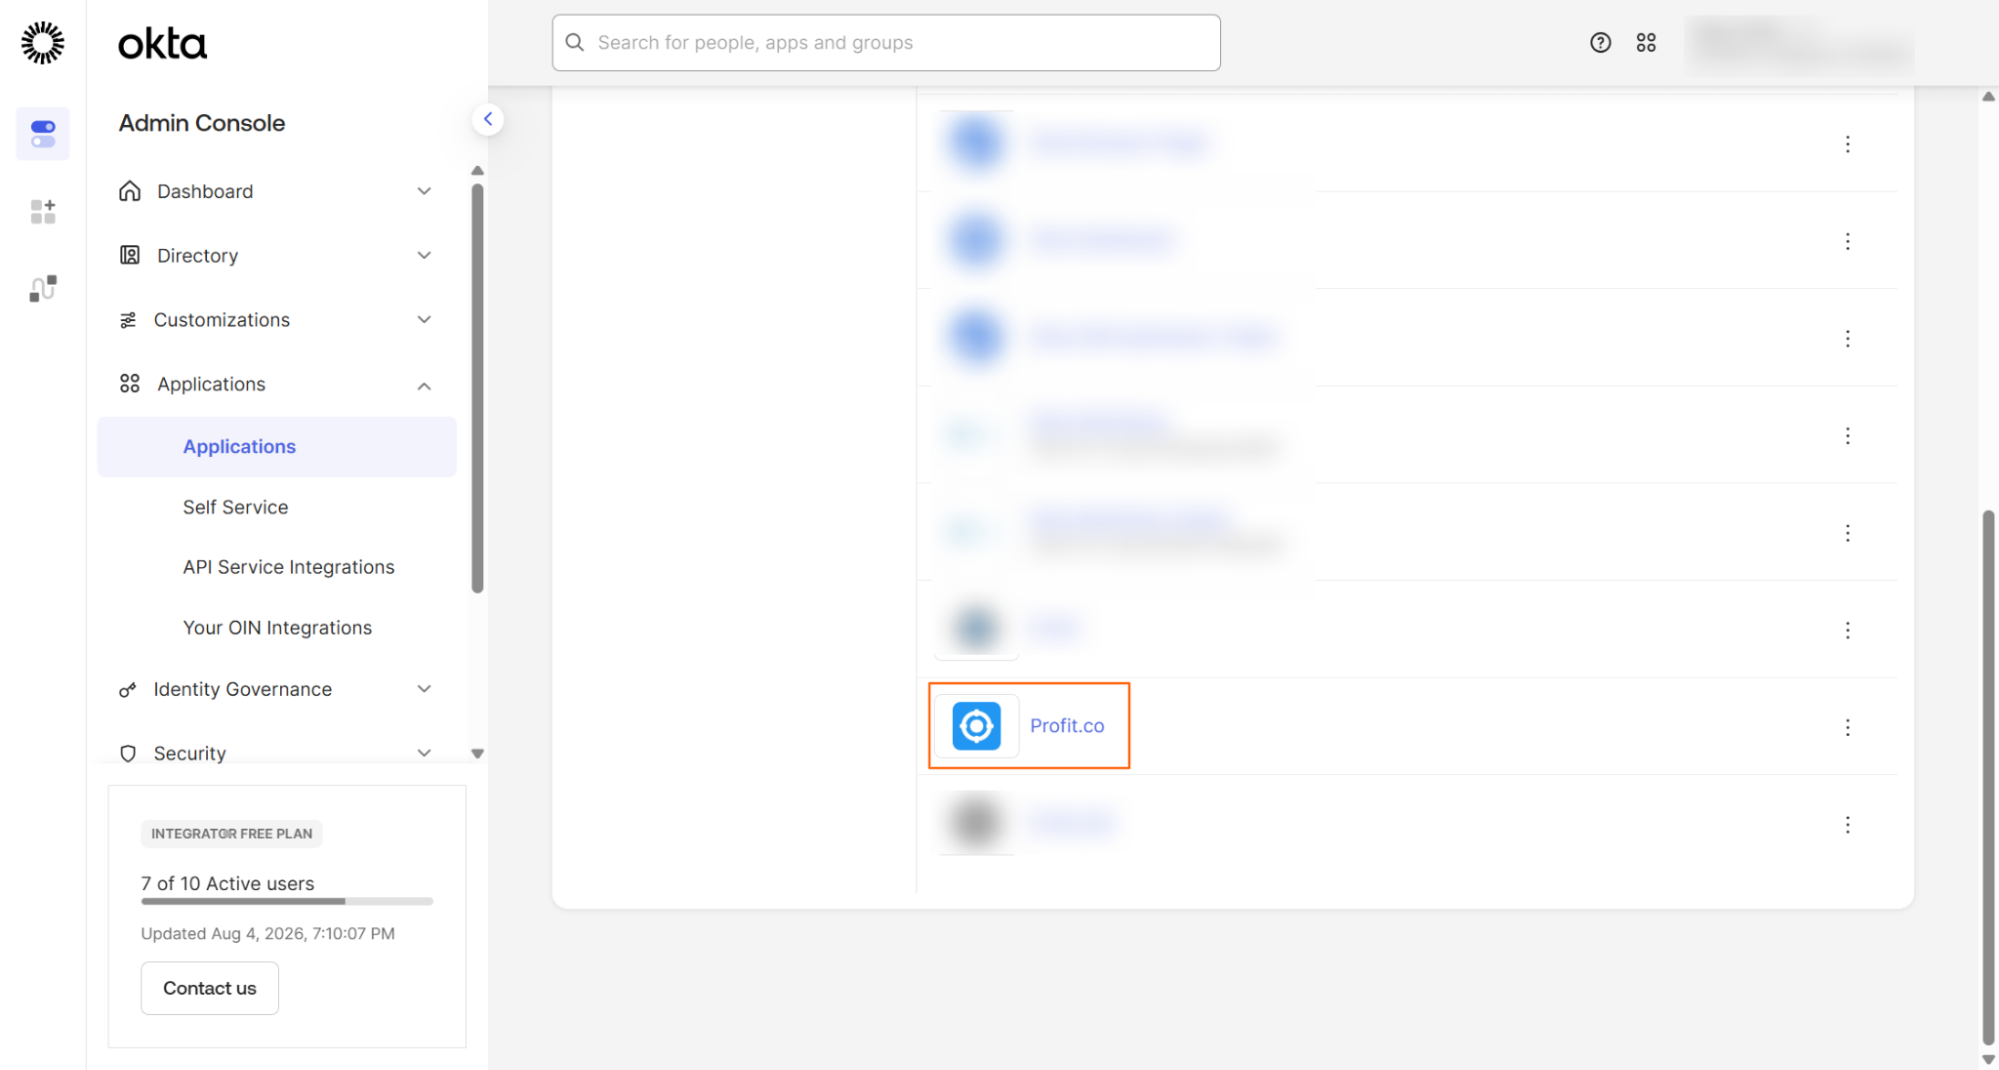
- Go to the Sign On tab.
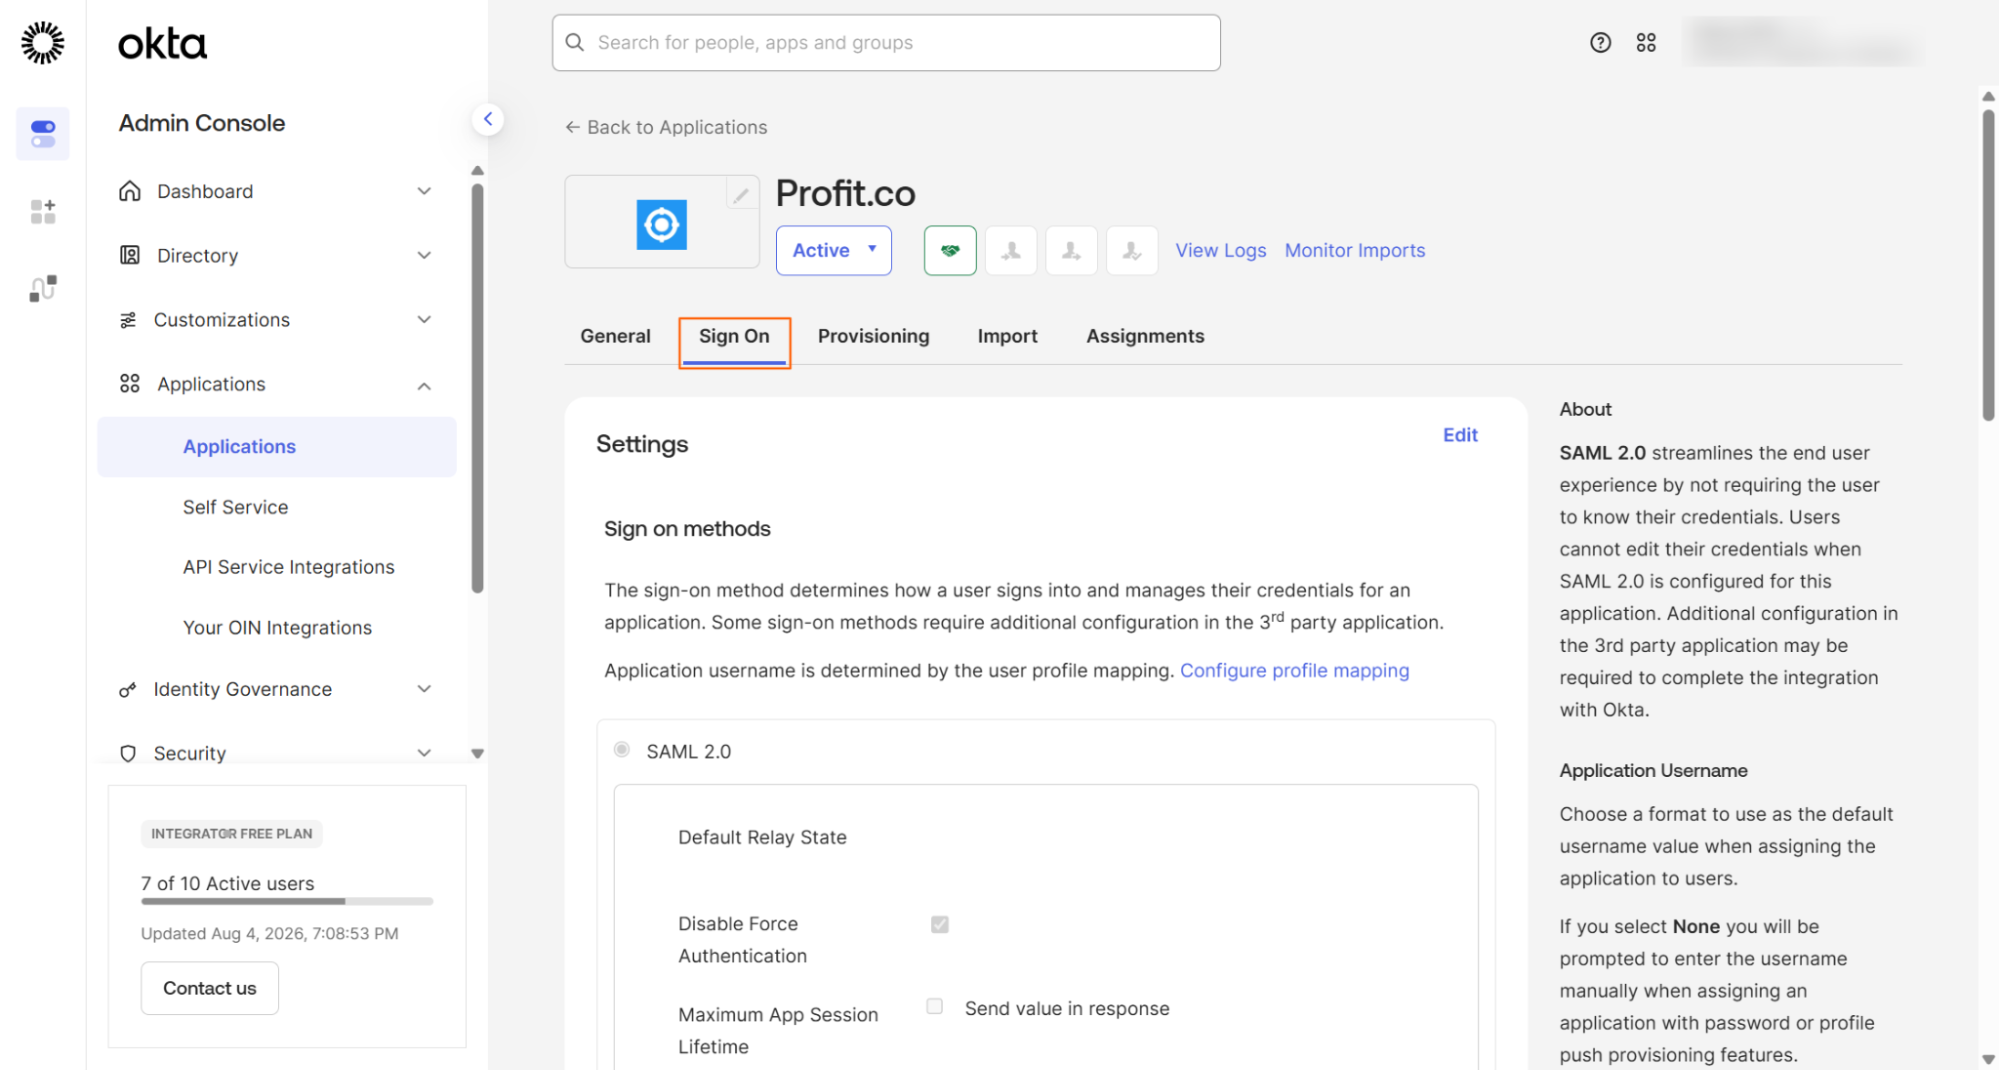
- Scroll down and click the View Setup Instructions button.
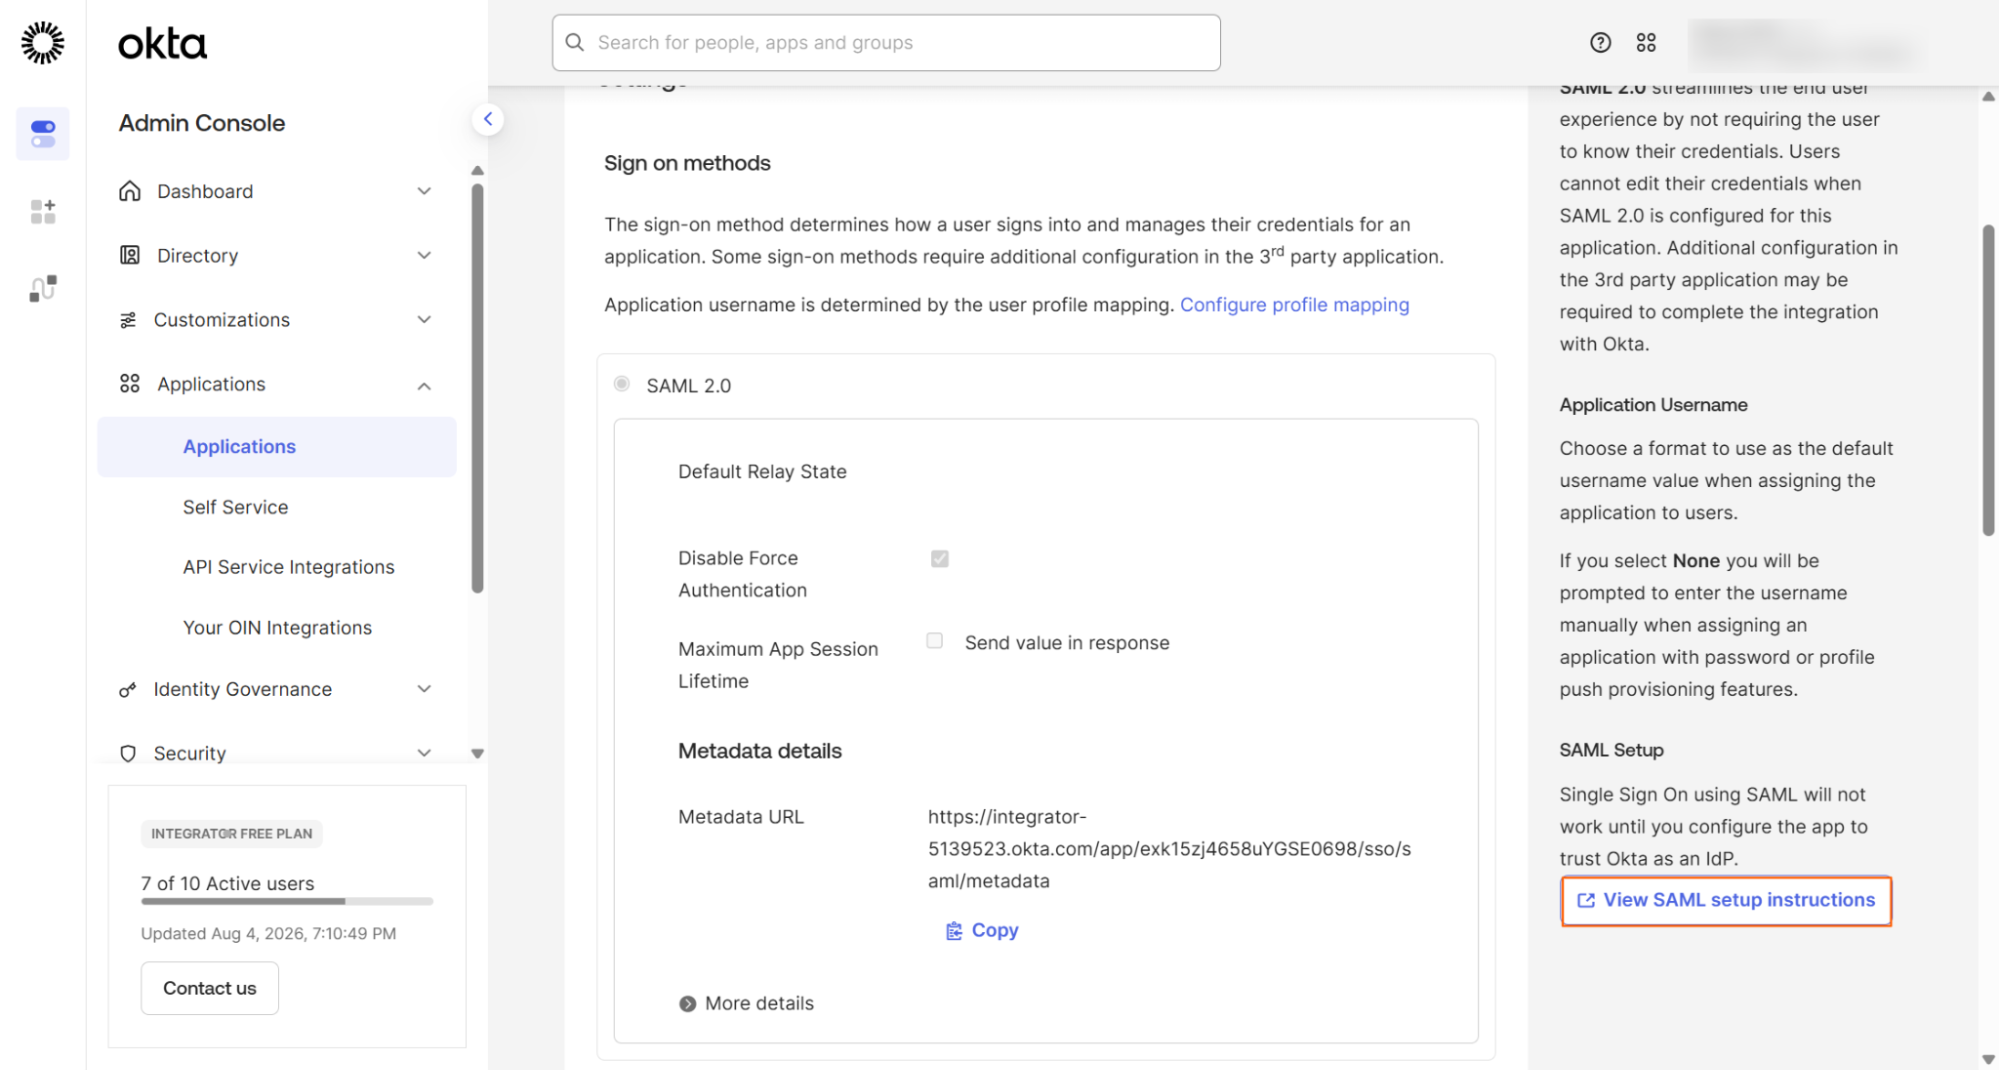
This opens the How to Configure SAML 2.0 for Profit.co instructions page, which contains the Issuer ID and X.509 Certificate required to complete the Profit.co side of the configuration.
Step 5
From the SAML 2.0 setup instructions page, collect the two values needed to register Okta in Profit.co.
- Scroll down on the setup instructions page.
- Copy the Issuer ID — this is the IDP Entity ID that Profit.co uses to identify Okta.
- Locate the X.509 Certificate block and copy the certificate content.
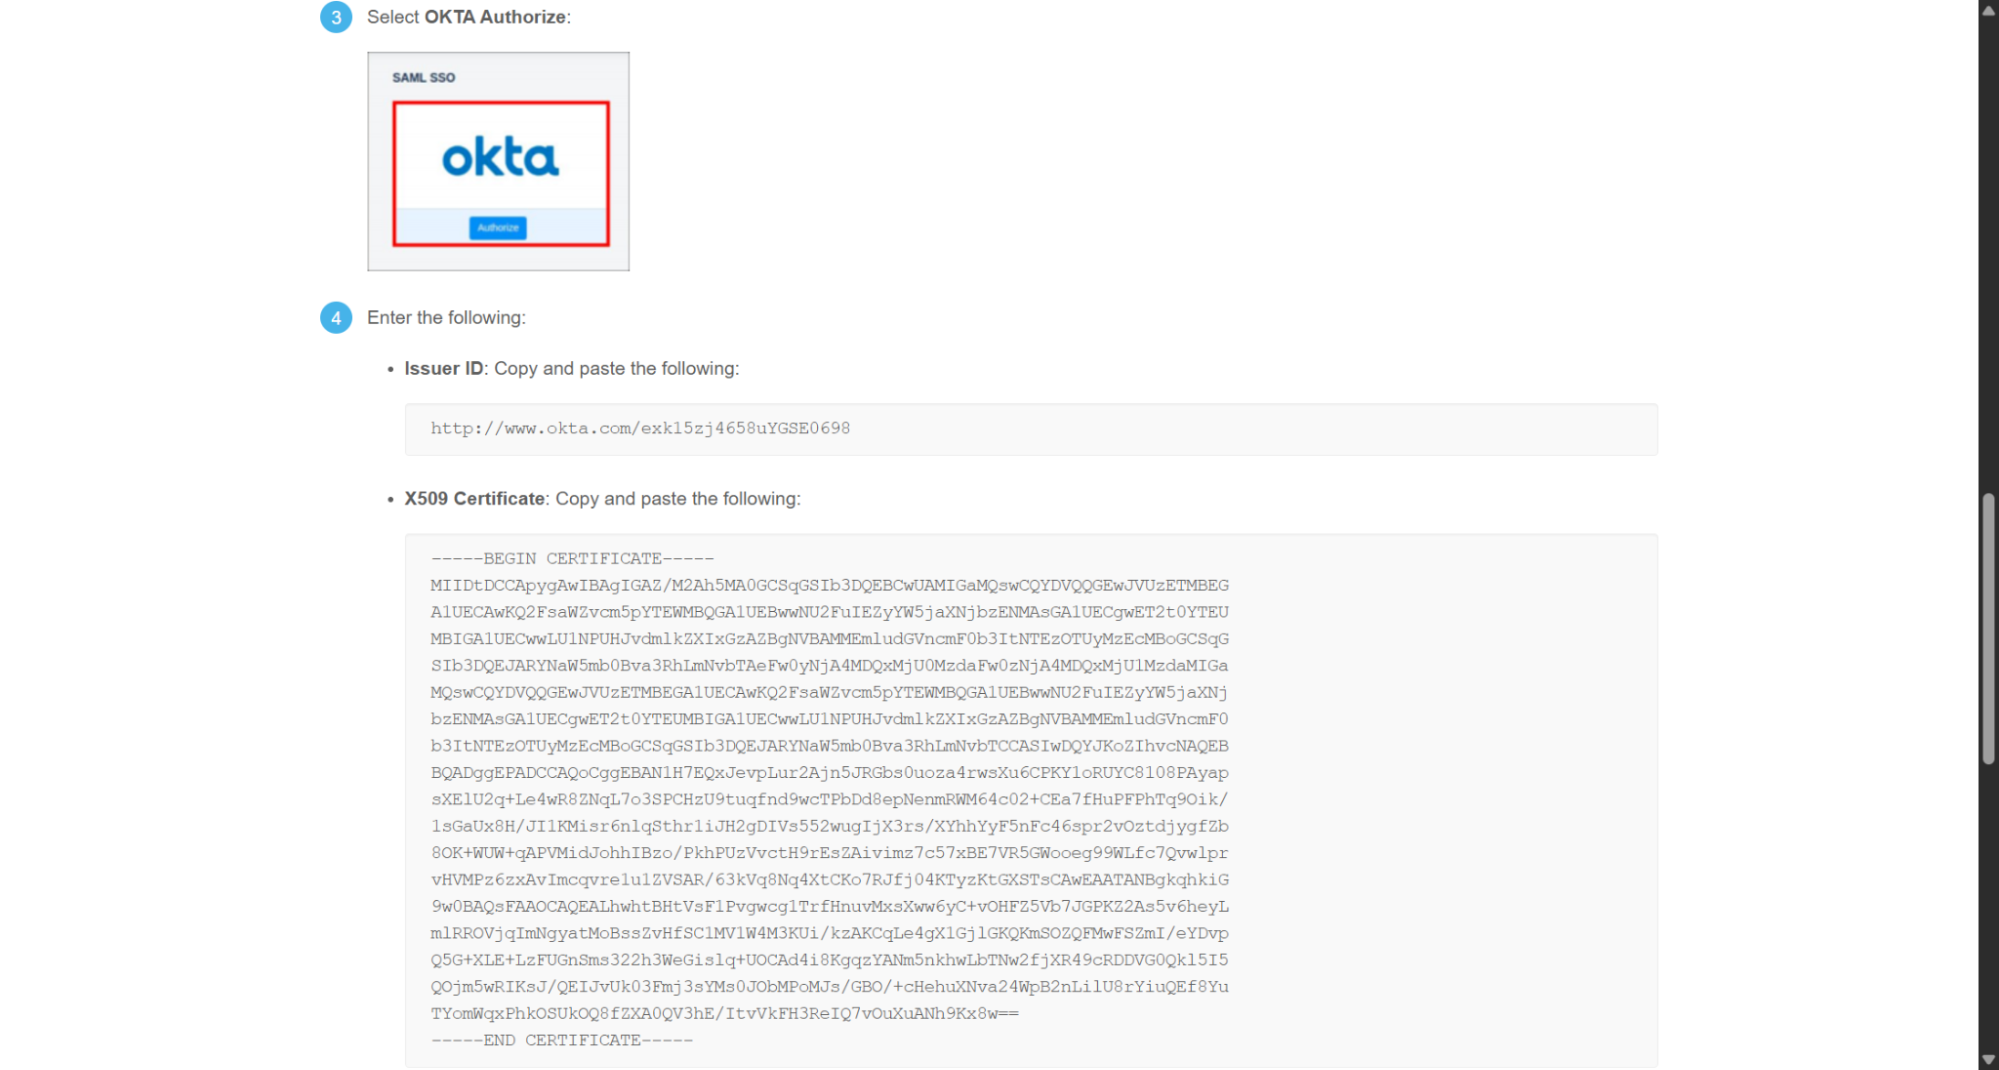
Note: Copy only the text between — and including — the lines BEGIN CERTIFICATE and END CERTIFICATE. Do not omit or truncate these header/footer lines.
Step 6
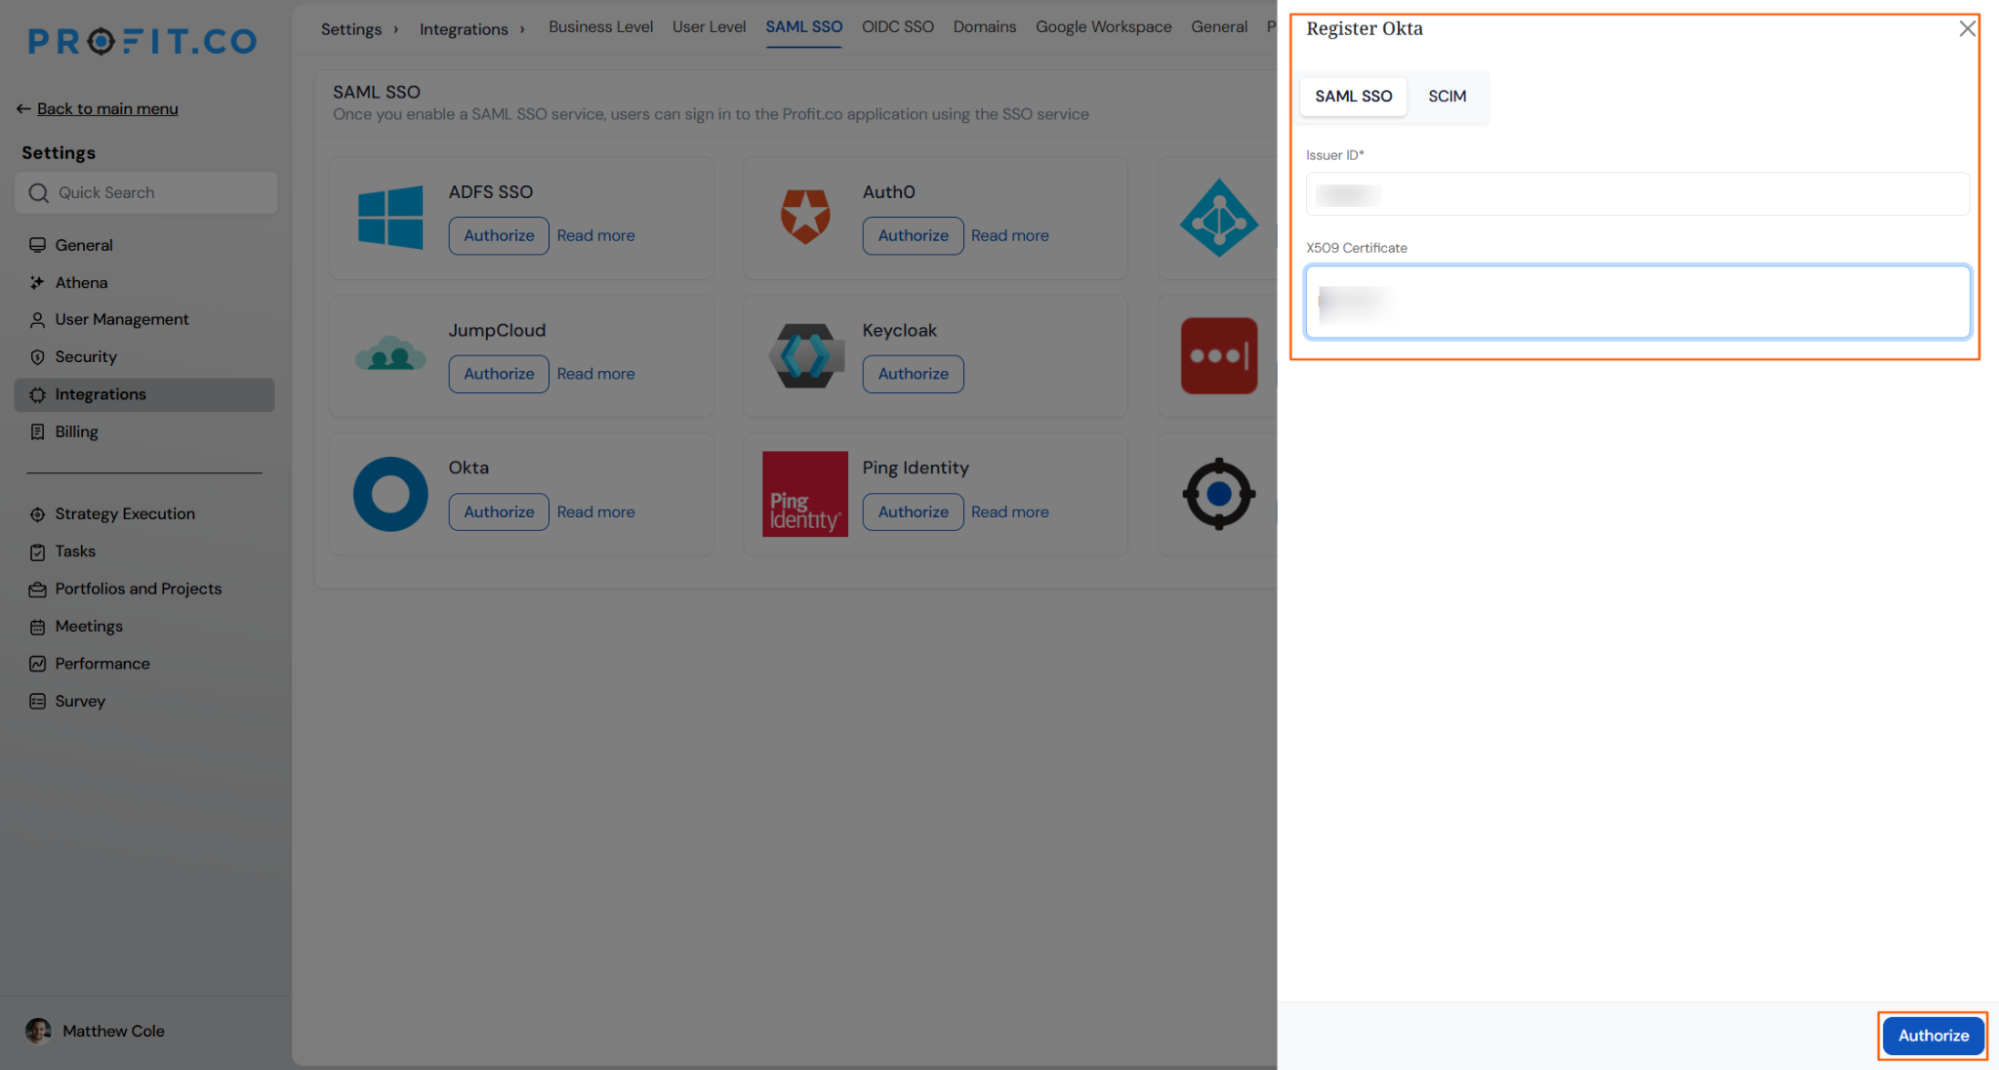
Enter the Issuer ID and X.509 Certificate in Profit.co to complete the SAML SSO configuration.
- Log in to Profit.co and navigate to Settings from the left navigation panel.
- Click Integrations.
- Select the SAML SSO tab.
- Locate Okta and click the Authorize button.
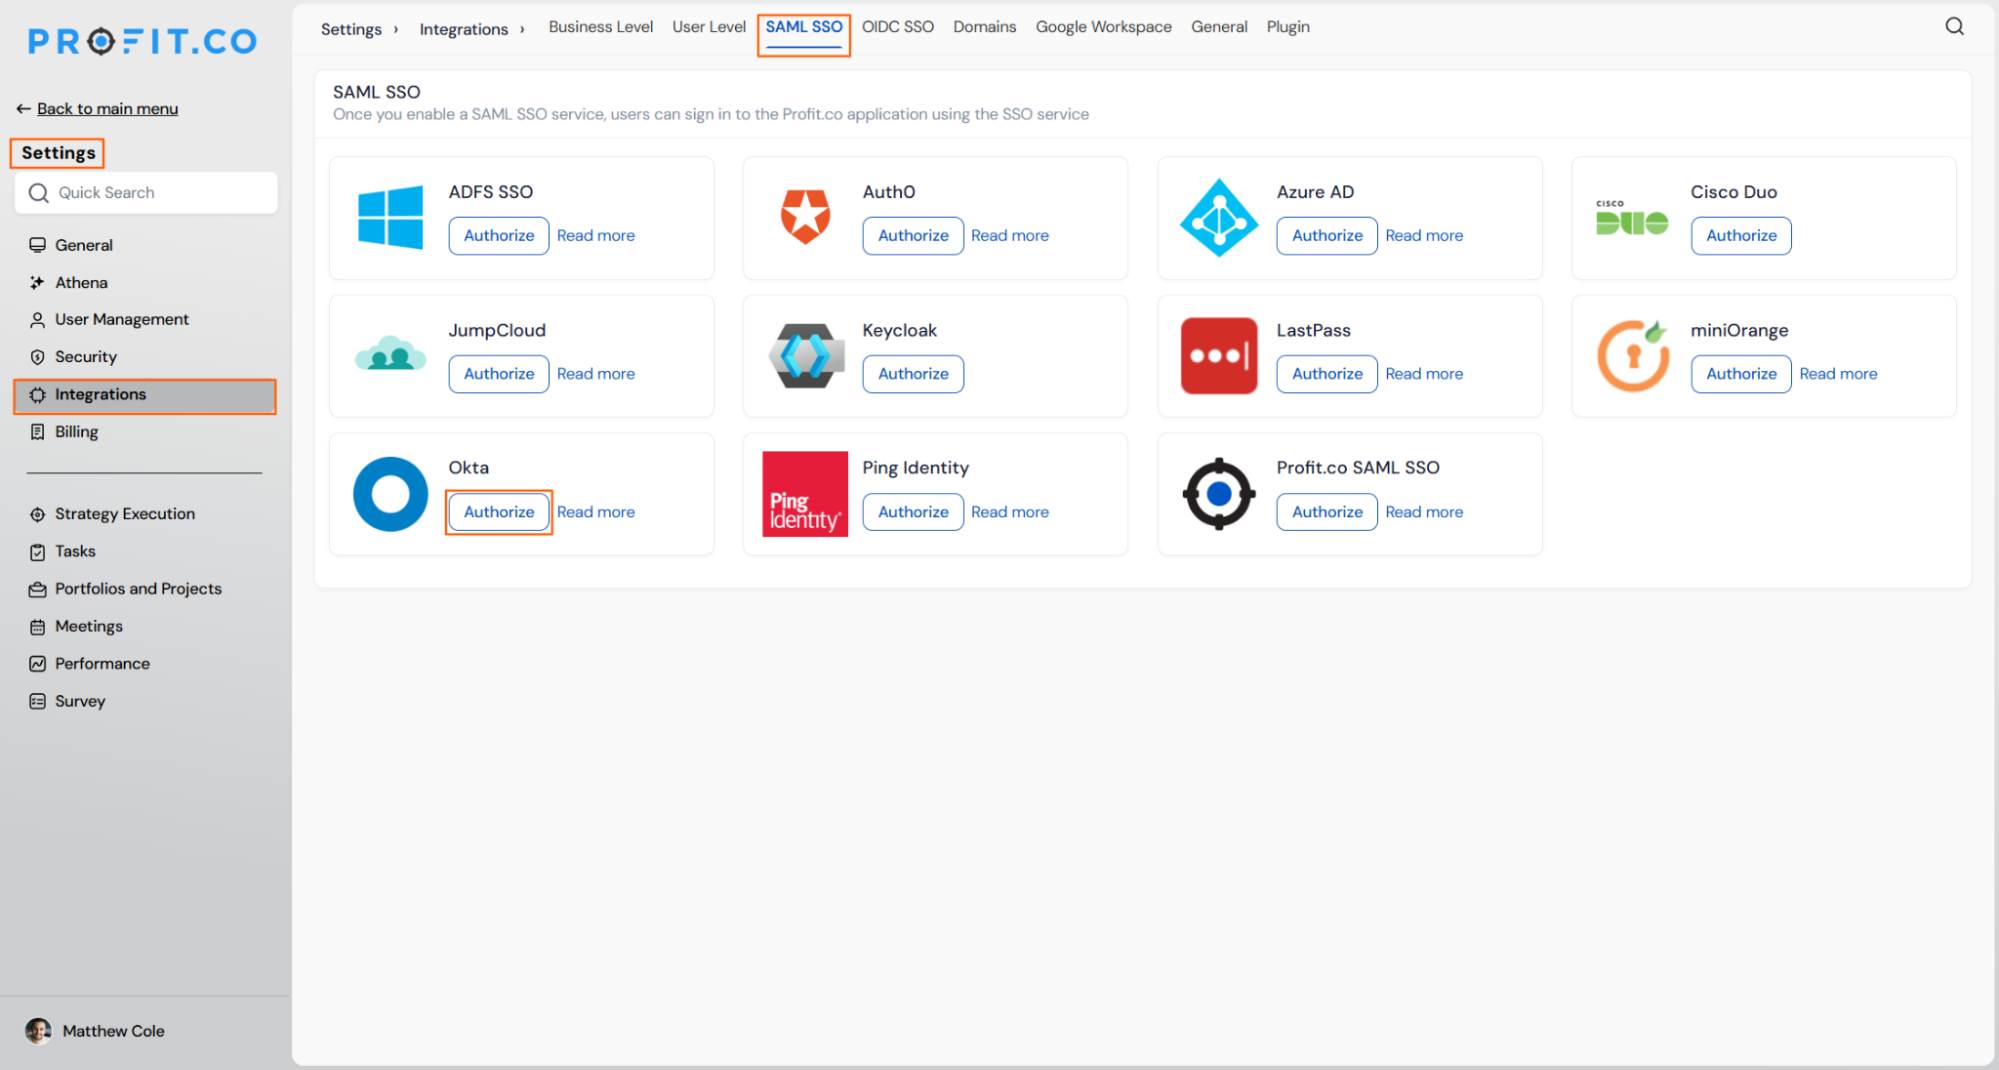
- Paste the Issuer ID into the Issuer ID field.
- Paste the X.509 Certificate into the Certificate field.
- Click Authorize to complete the SSO registration.
Step 7
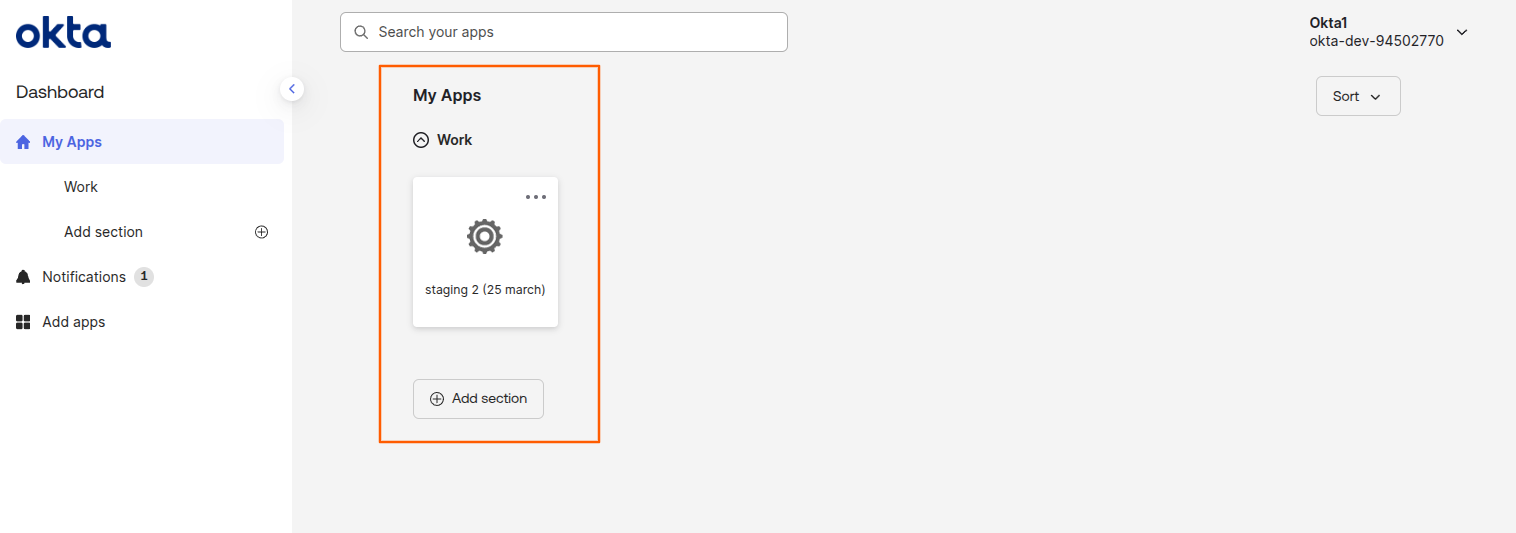
- Switch to the Okta End-User Dashboard tab in your browser.
- Click on My Apps — the Profit.co app should be visible.
- Click the Profit.co app tile. You should be taken directly into Profit.co without being prompted for a username or password.
Note: If users are not redirected correctly, verify that the Issuer ID and X.509 Certificate in Profit.co exactly match the values from the Okta SAML setup instructions page.
Configure Okta User Provisioning for Profit.co
SCIM-based provisioning keeps Profit.co user accounts automatically in sync with your Okta directory. The following lifecycle events are supported:
- Push New Users: Users assigned to the Profit.co app in Okta are automatically created in Profit.co User Management.
- Push Profile Updates: Changes to user profiles in Okta are automatically pushed to Profit.co in real time.
- Push User Deactivation: Deactivating a user in Okta or removing their access to the Profit.co app deactivates the user in Profit.co.
- Reactivate Users: Restoring access to the Profit.co app in Okta reactivates the user’s Profit.co account.
Requirements
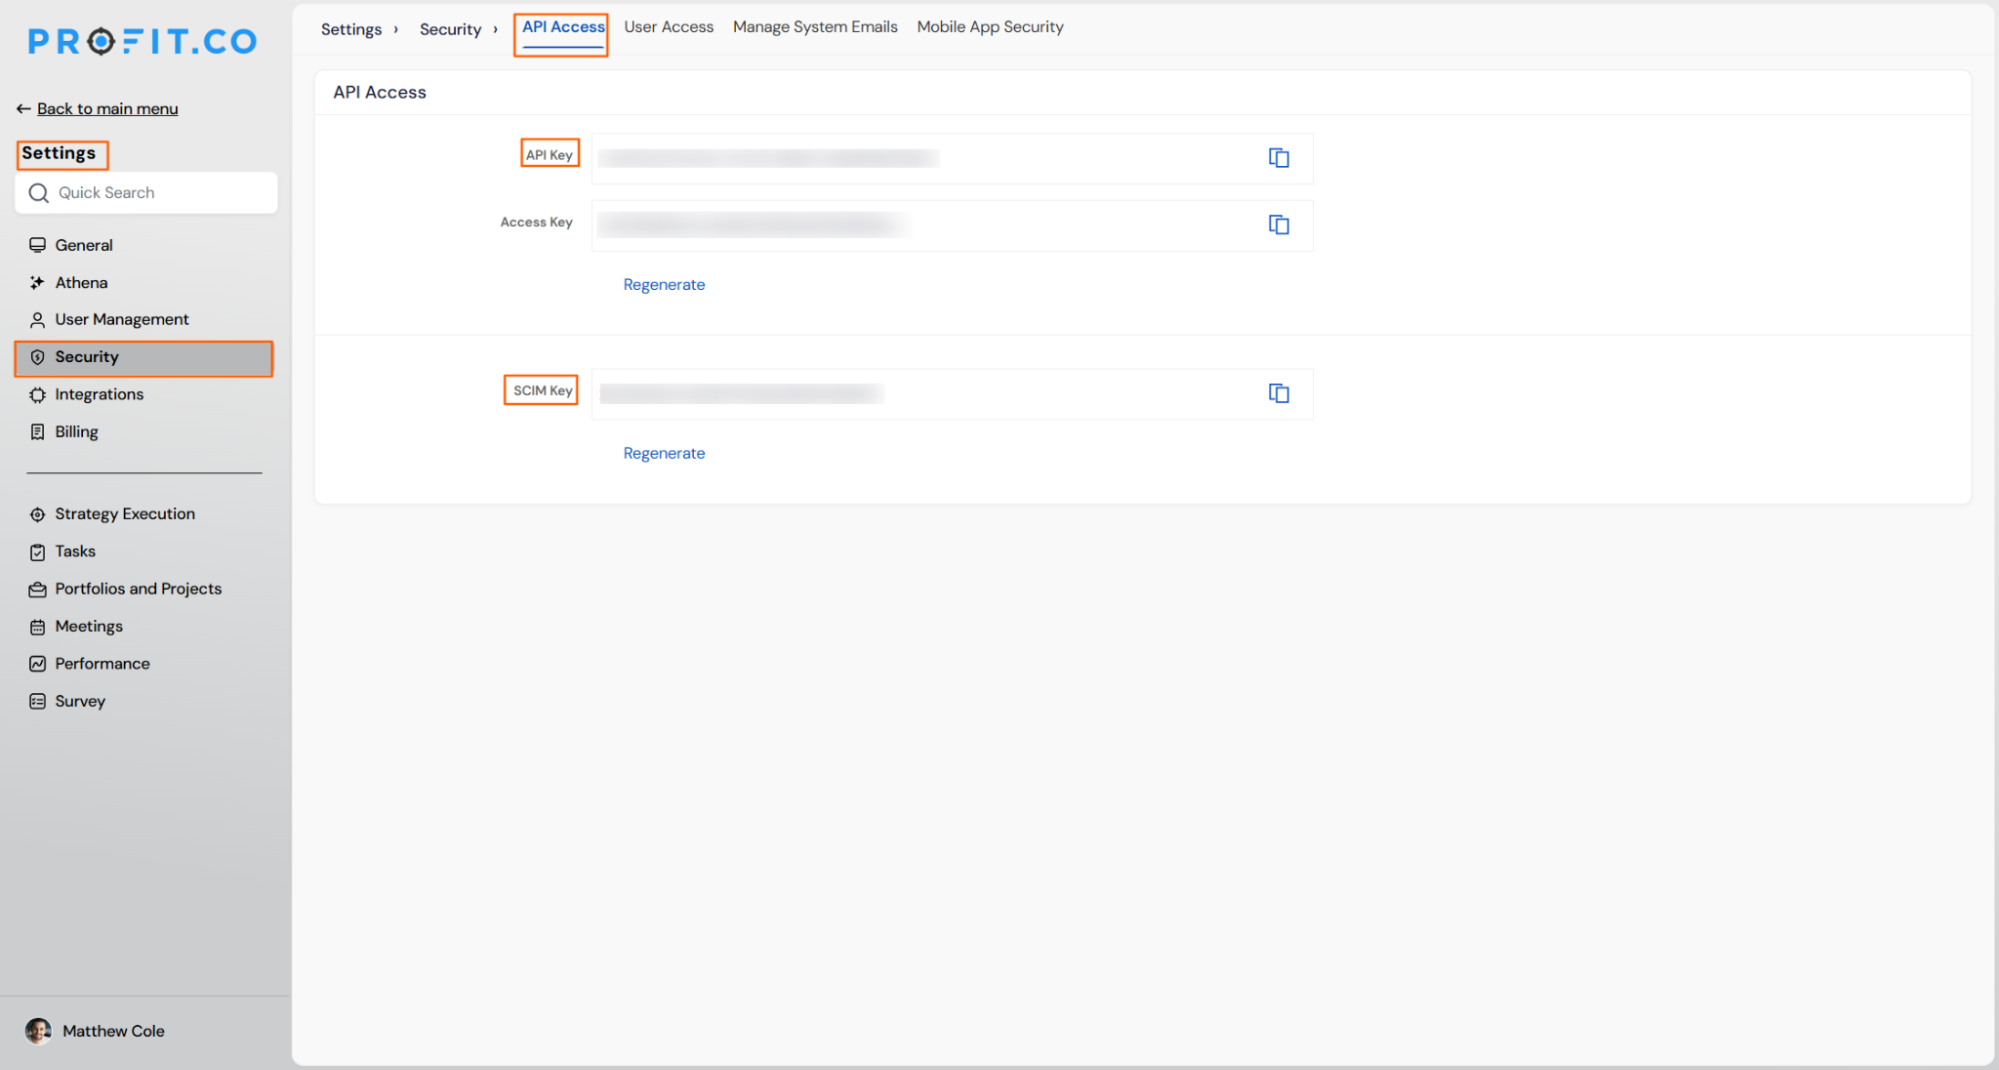
You need Admin access in Profit.co to retrieve the API Key and SCIM Key required to form the Bearer Token.
- Navigate to Settings -> Security -> API Access in Profit.co
- Copy your API Key and SCIM Key
- Form the API Token using the format: API_KEY:SCIM_KEY
Step 1
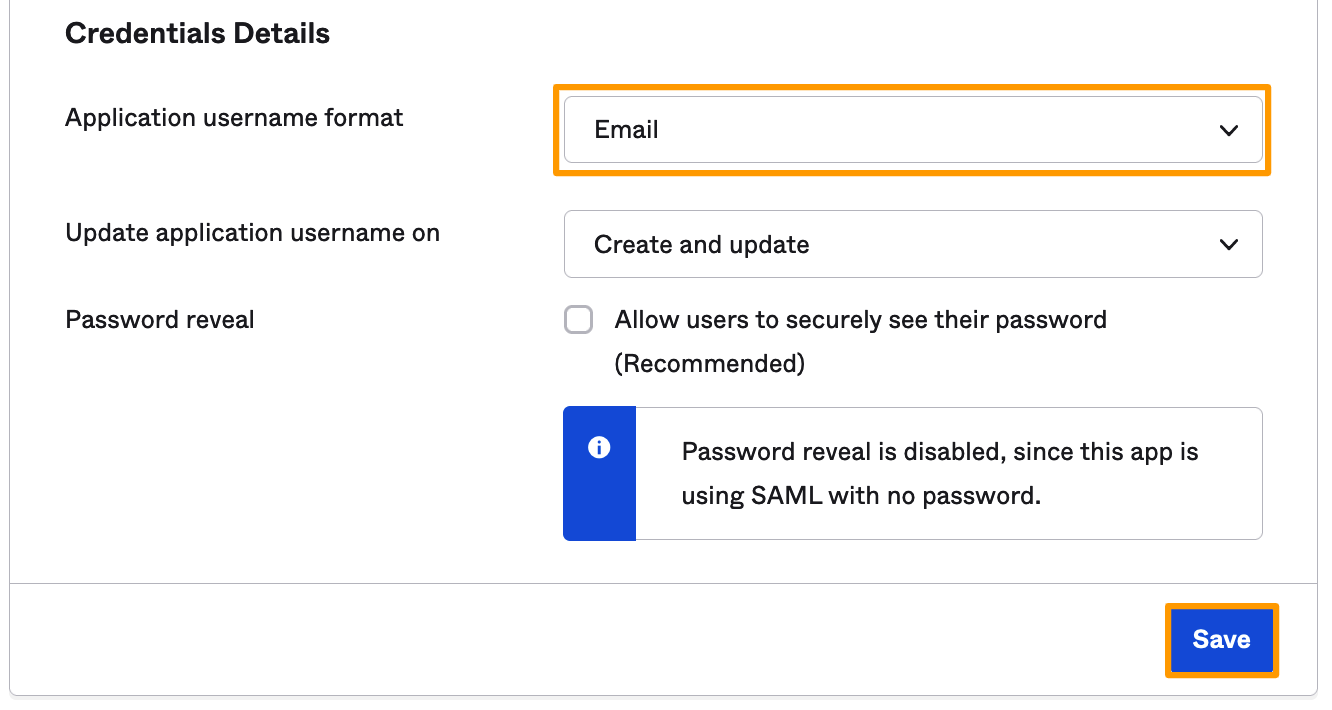
Ensure Okta sends the correct user identifier to Profit.co during provisioning.
- Open the installed Profit.co app in Okta.
- Go to the Sign On tab.
- Locate the Application username format setting.
- Select Email as the username format.
- Click Save.
Step 2
Connect Okta to Profit.co’s SCIM endpoint using your API credentials.
- Go to the Provisioning tab within the Profit.co app in Okta.
- Click the Edit button.
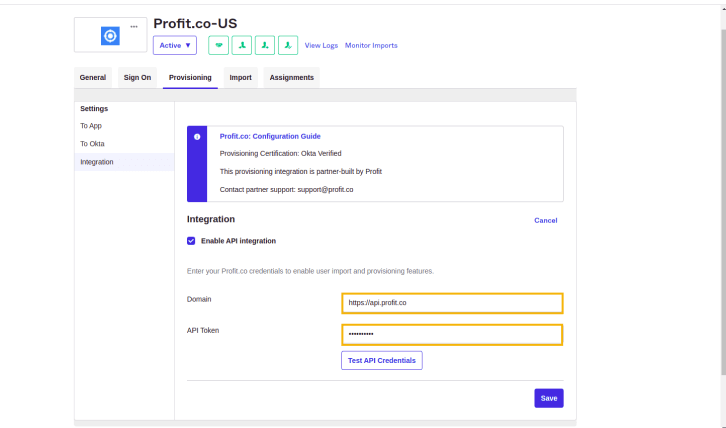
- Enter the Domain (SCIM Base URL) for your Profit.co region:
Region SCIM Base URL / Domain US Region https://app.profit.co/app/rest/platform/auth/scim/v2EU Region https://eu2-app.profit.co/app/rest/platform/auth/scim/v2ME Region https://me1-app.profit.co/app/rest/platform/auth/scim/v2SA Region https://sa1-app.profit.co/app/rest/platform/auth/scim/v2- Enter the API Token in the following format:
Note: The API Key and SCIM Key are available in Profit.co under Settings -> Security -> API Access. Separate them with a colon with no spaces: API_KEY:SCIM_KEY.
Step 3
Activate all provisioning actions and validate the SCIM connection before going live.
- In the Provisioning to App section, click the Edit button.
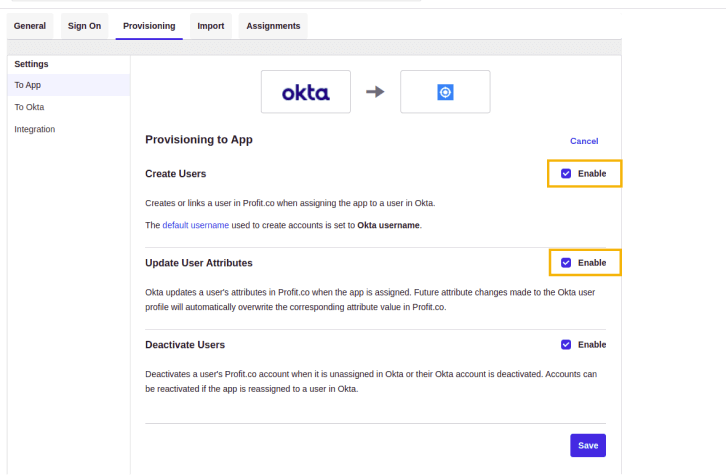
- Enable all provisioning checkboxes (Create Users, Update User Attributes, Deactivate Users).
- Click Test API Credentials to verify the connection between Okta and Profit.co.
- Once the test passes successfully, click Save to apply the configuration.
Supported attributes for sync:
Okta Attribute Profit.co Field Required Username userName
Yes
Given Name firstName
Yes
Family Name lastName
Yes
Primary Email email
Yes
Primary Email Type emailType
No
Department department
No
Job Title title
No
Active Status active
Yes
Department Sync
- Existing Departments: If the department already exists in Profit.co, the user will be assigned to it unless the department is disabled, and no duplicate departments will be created.
- New Departments: If the department does not exist in Profit.co, it will be automatically created and the user will be assigned to it during provisioning.
- Department and Sub-Department Sync: When a user is synced with both Department and Sub-Department attributes, the system first checks if the Department exists; if it does, the Sub-Department is created under it and the user is assigned to it, and if the Department does not exist, the system checks the user’s already associated Department and creates the Sub-Department under it if available, then assigns the user to that Sub-Department.
- Only Sub-Department Sync: If a user is synced with only the Sub-Department attribute, the system checks whether the corresponding associated Department exists; if it does not exist, the user will still be created, but the Department and Sub-Department fields will not be synced.
- Cross-Functional Department Mapping: To assign users to multiple departments, map the department field with comma-separated values. Profit.co automatically associates the user with all specified departments during SCIM provisioning.
Role Sync
When any of the roles listed below are selected, the same role will be automatically reflected in Profit.co.
SCIM Role Profit.co Role manager Profit Manager
user Profit User
read Only Profit Read Only
department Access Only Department Access Only
Configure Custom Role Attributes via SCIM
Okta allows you to define a custom role attribute and sync it to Profit.co via SCIM, so the correct Profit.co role is automatically assigned when a user is provisioned.
Step 1
Create a custom attribute named role in both the Okta User Profile and the Profit.co Application Profile.
Okta User Profile
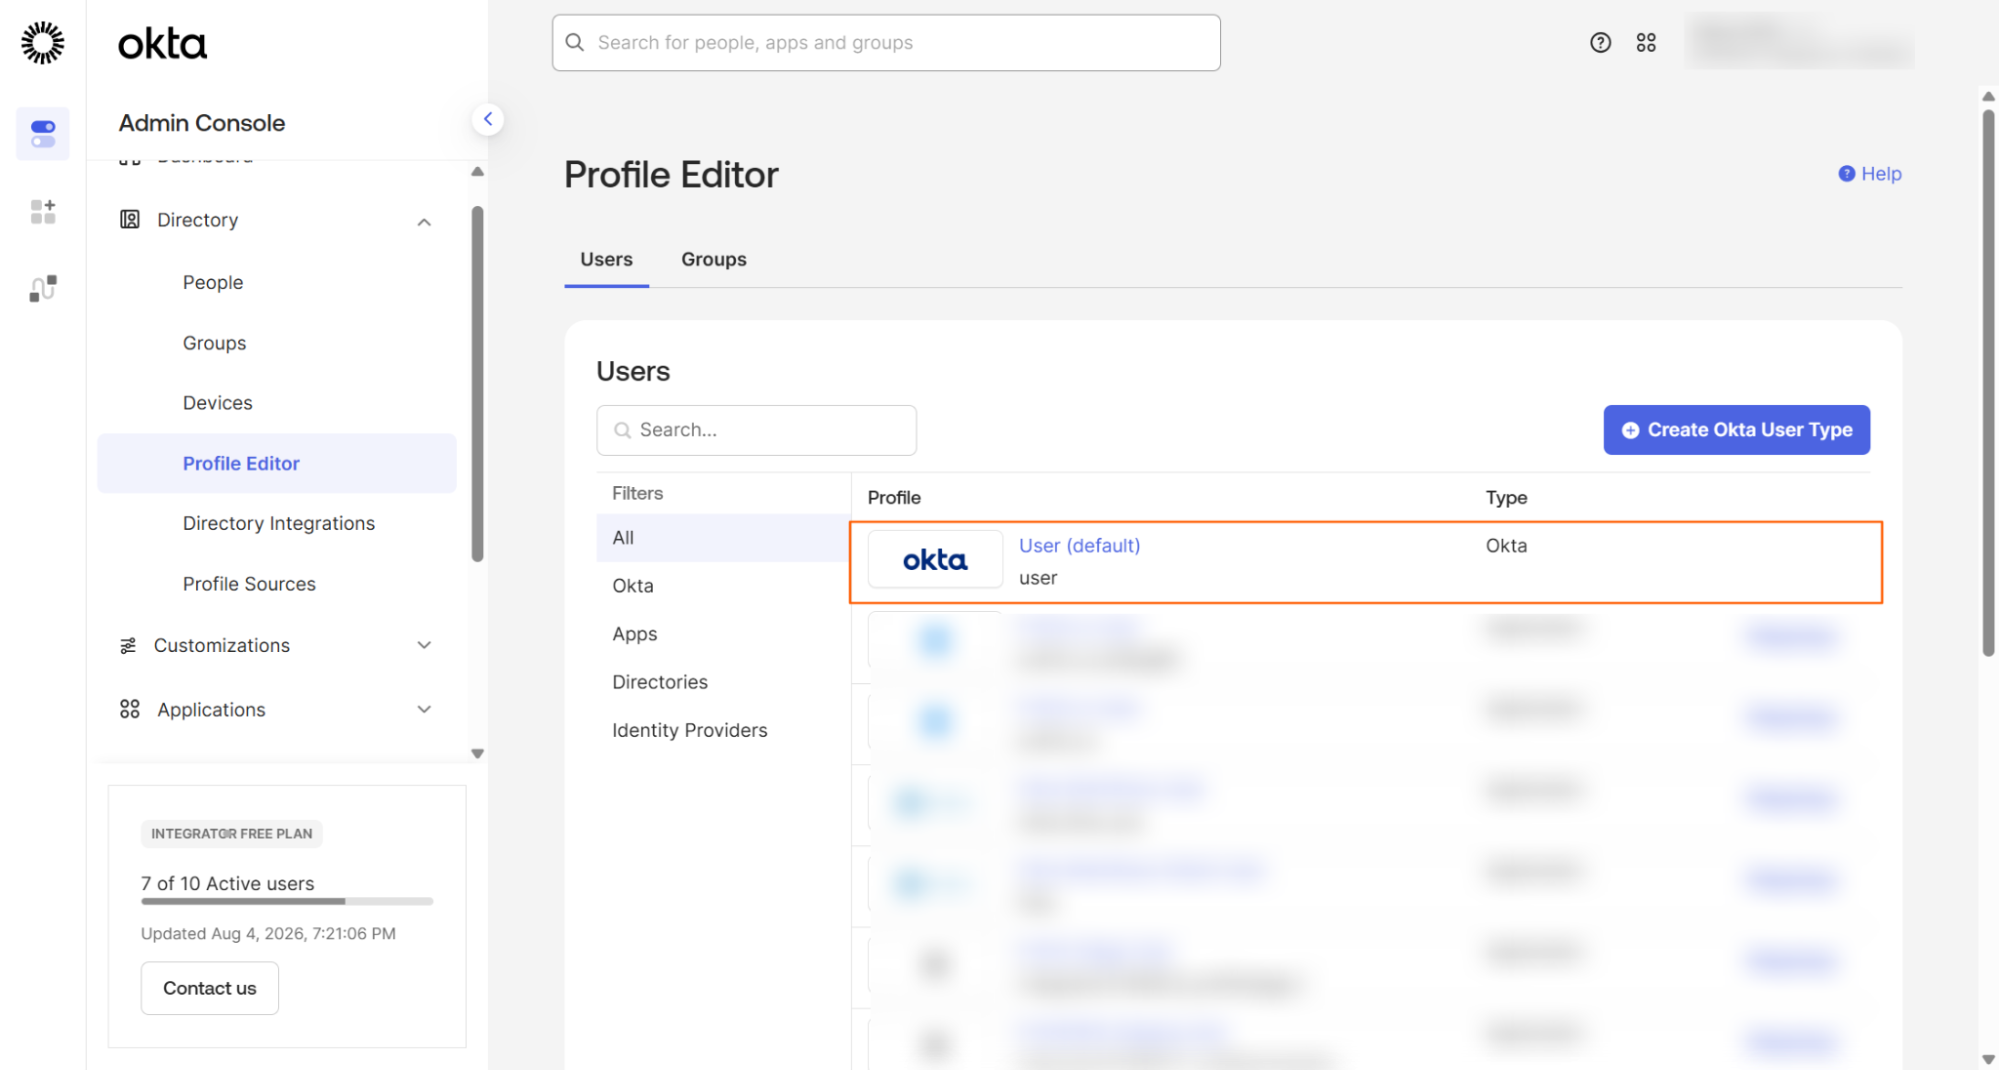
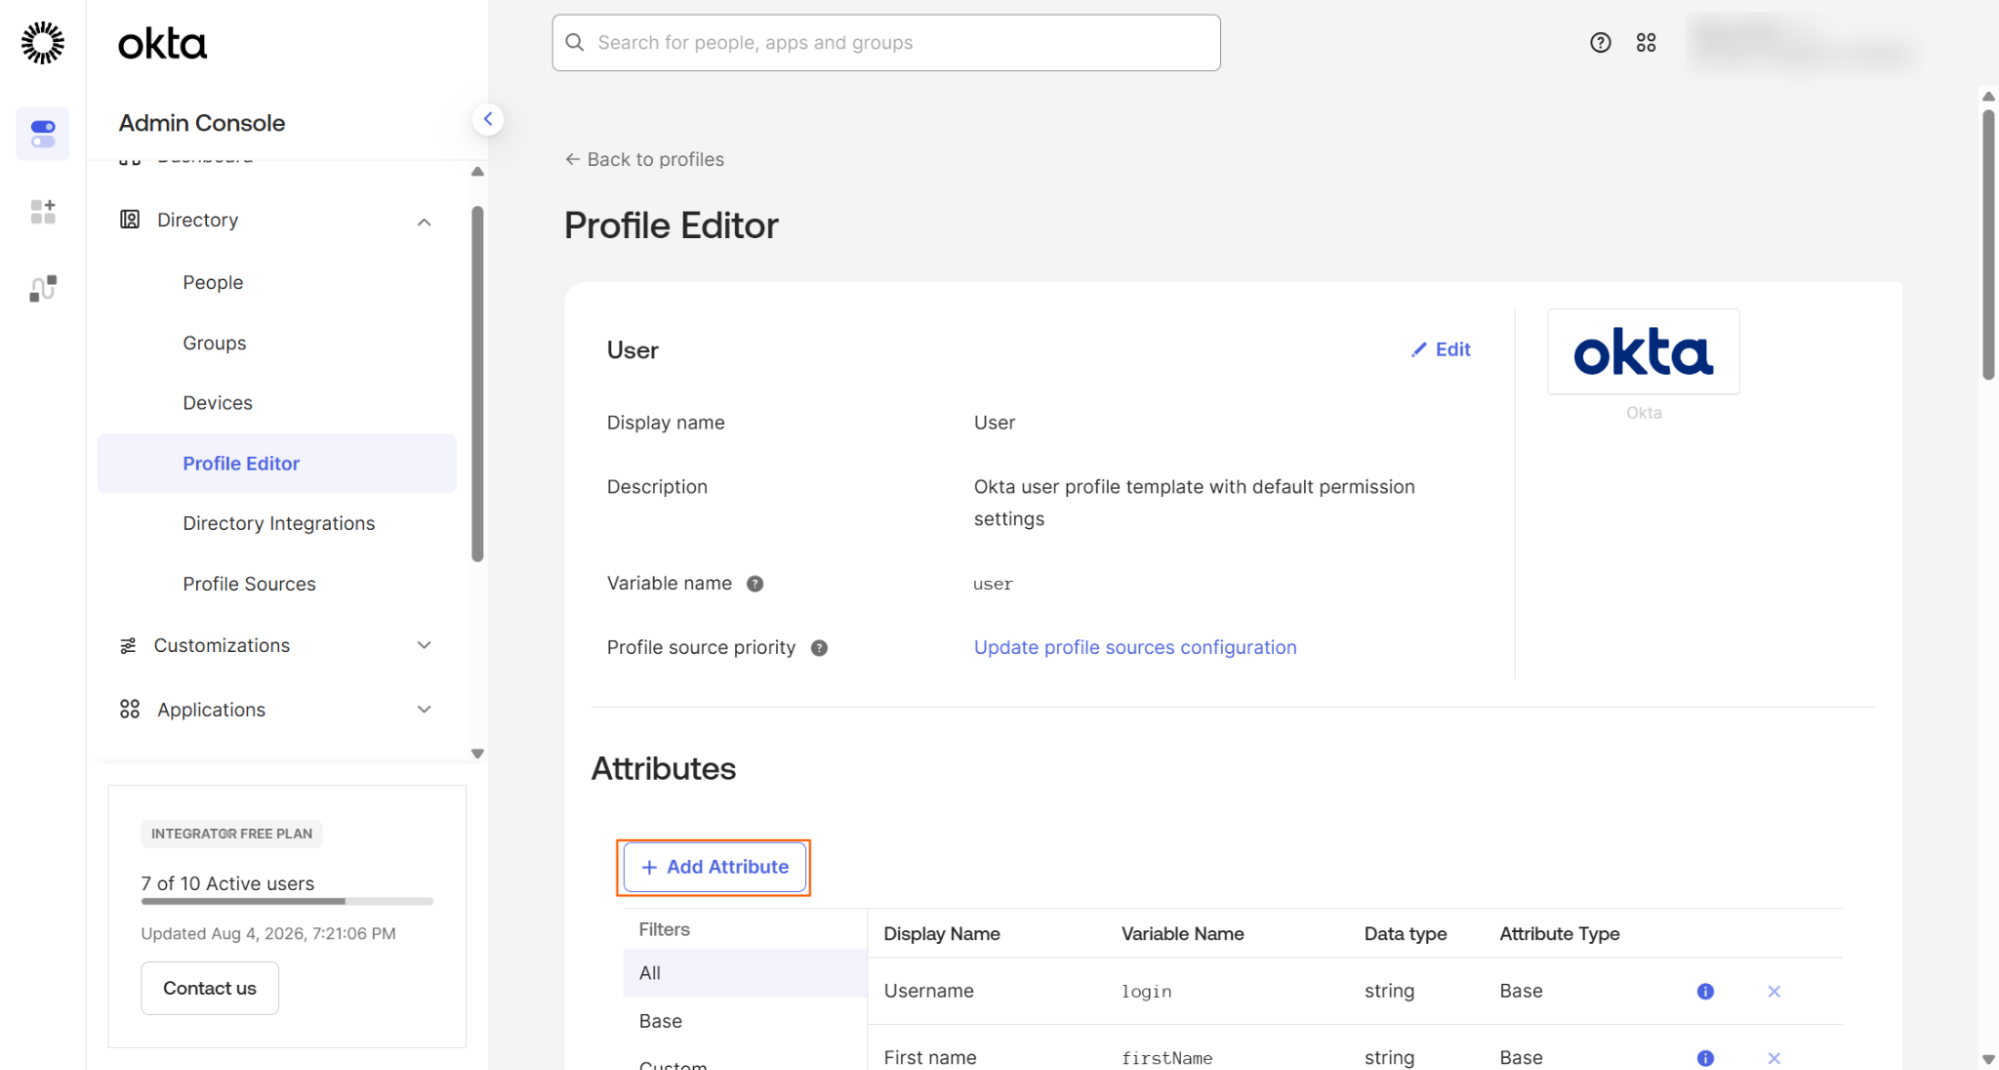
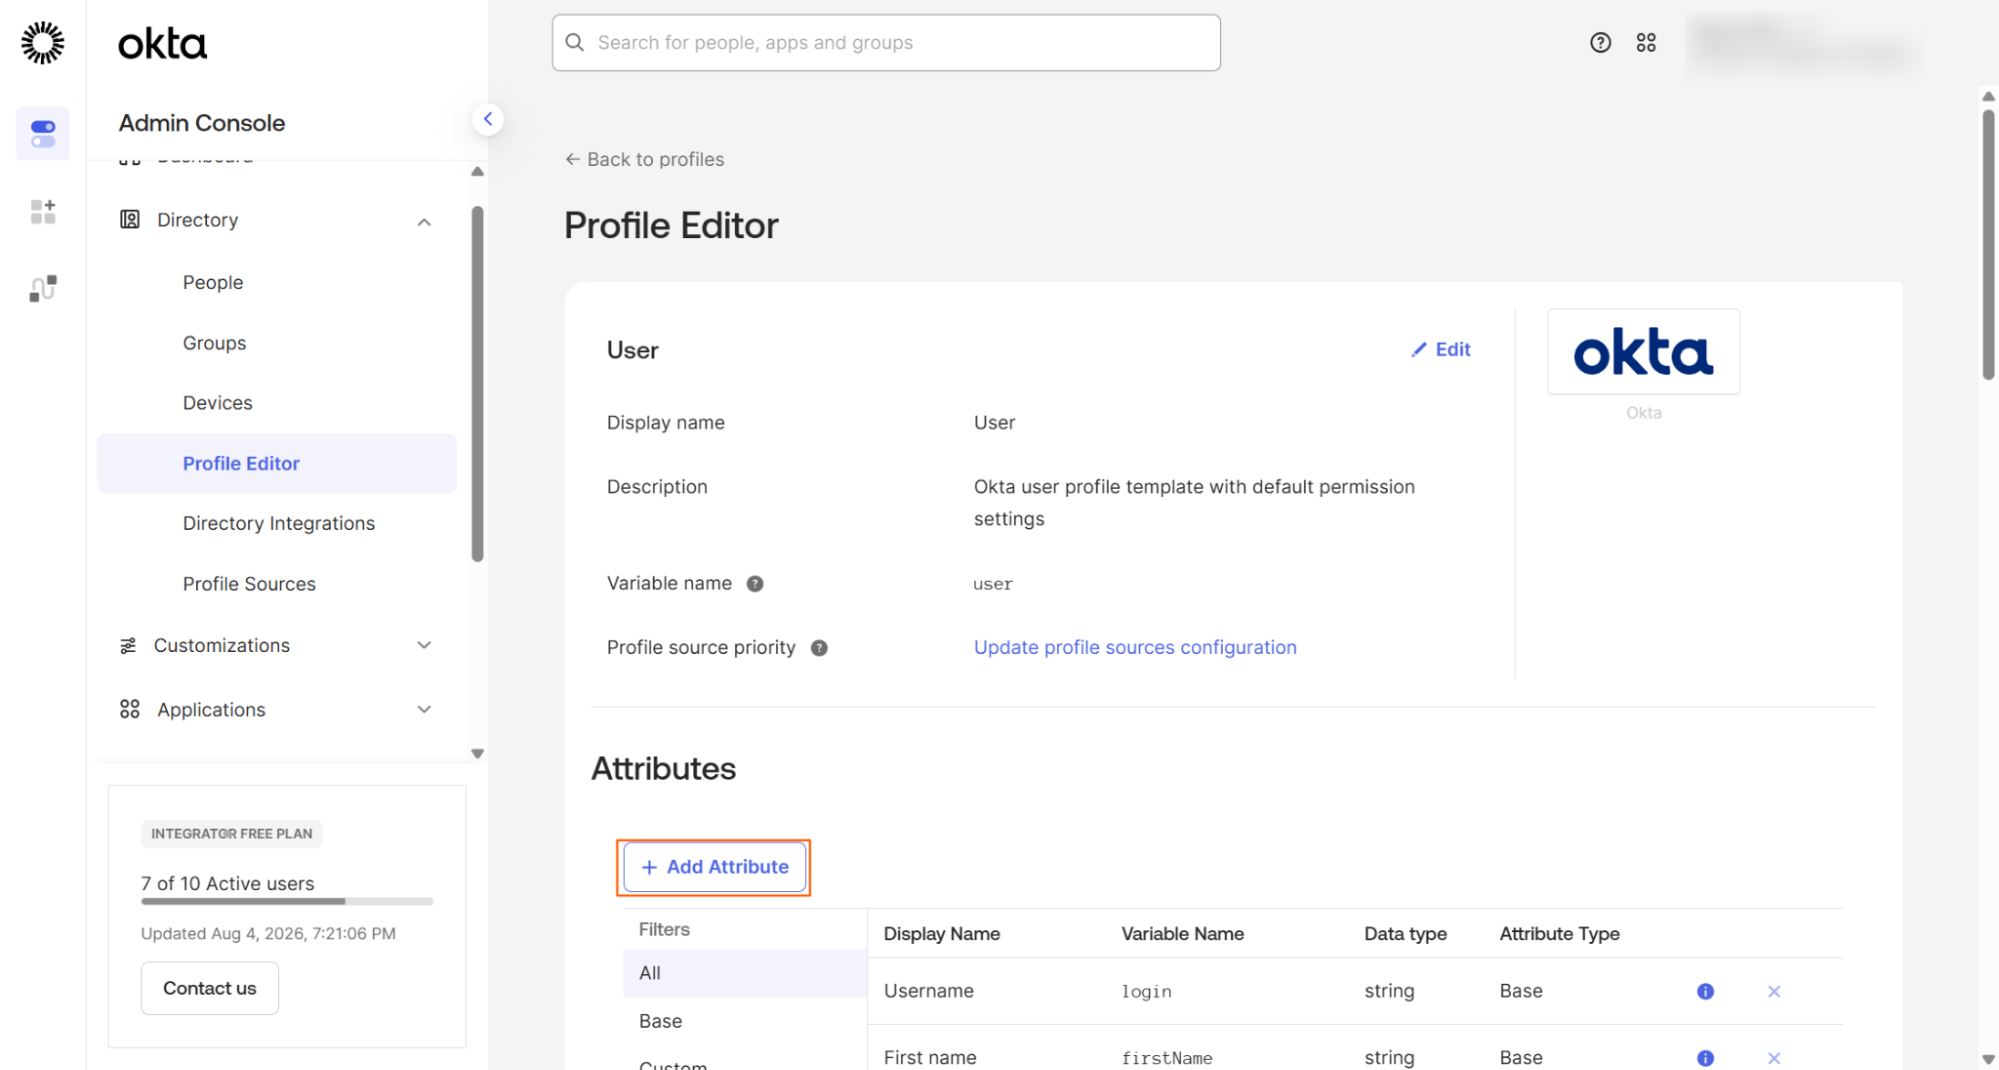
- Navigate to Directory -> Profile Editor -> Okta User (default) and click + Add Attribute.
- Set the Display Name and Variable Name to role. (Note: The Variable Name must be role — all lowercase.)
- Set User Permission to Read Only and click Save.
Profit.co Application Profile
- Navigate to Directory -> Profile Editor -> OKTA SCIM App and click + Add Attribute.
- Set the External Namespace as required for your configuration.
- Set User Permission to Read Only and click Save.
Step 2
Set up the attribute mapping so the role value flows from the Okta user profile to Profit.co on every sync.
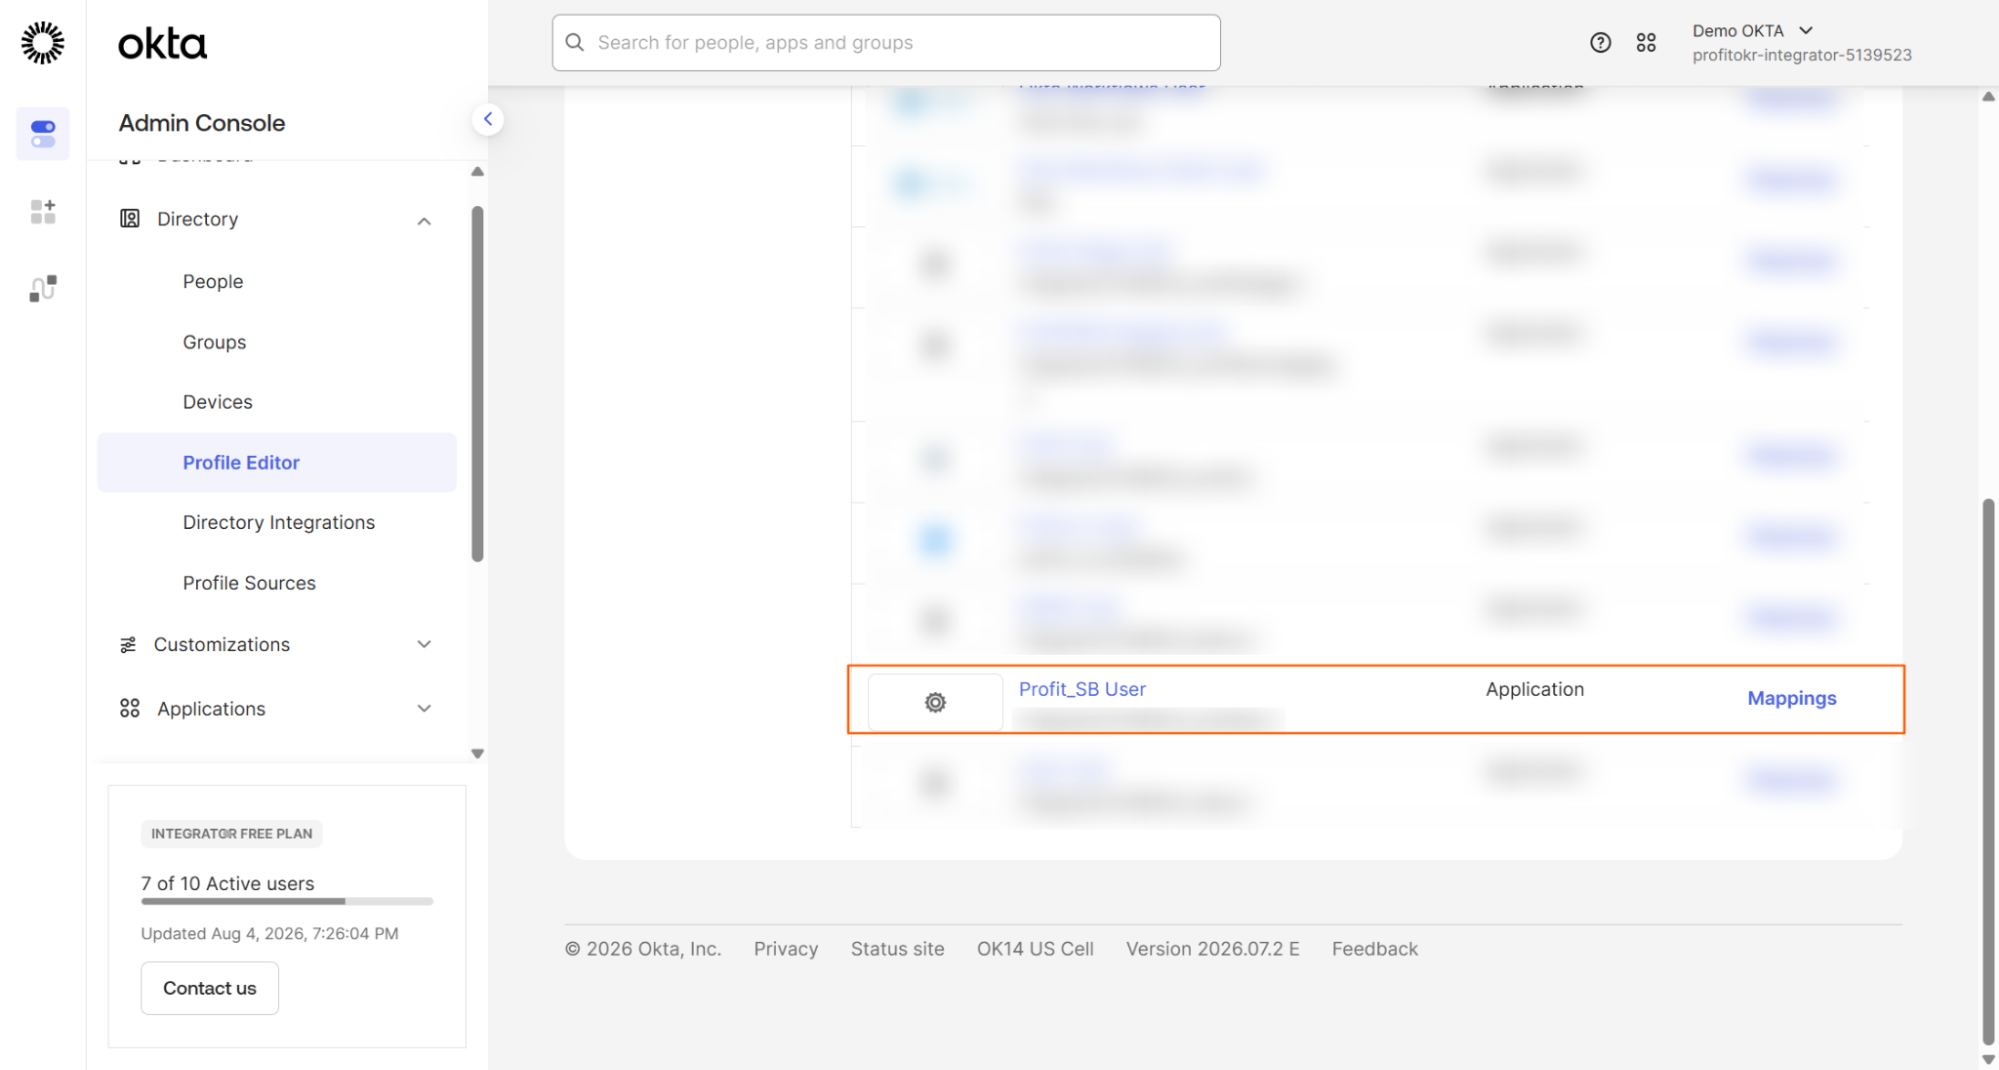
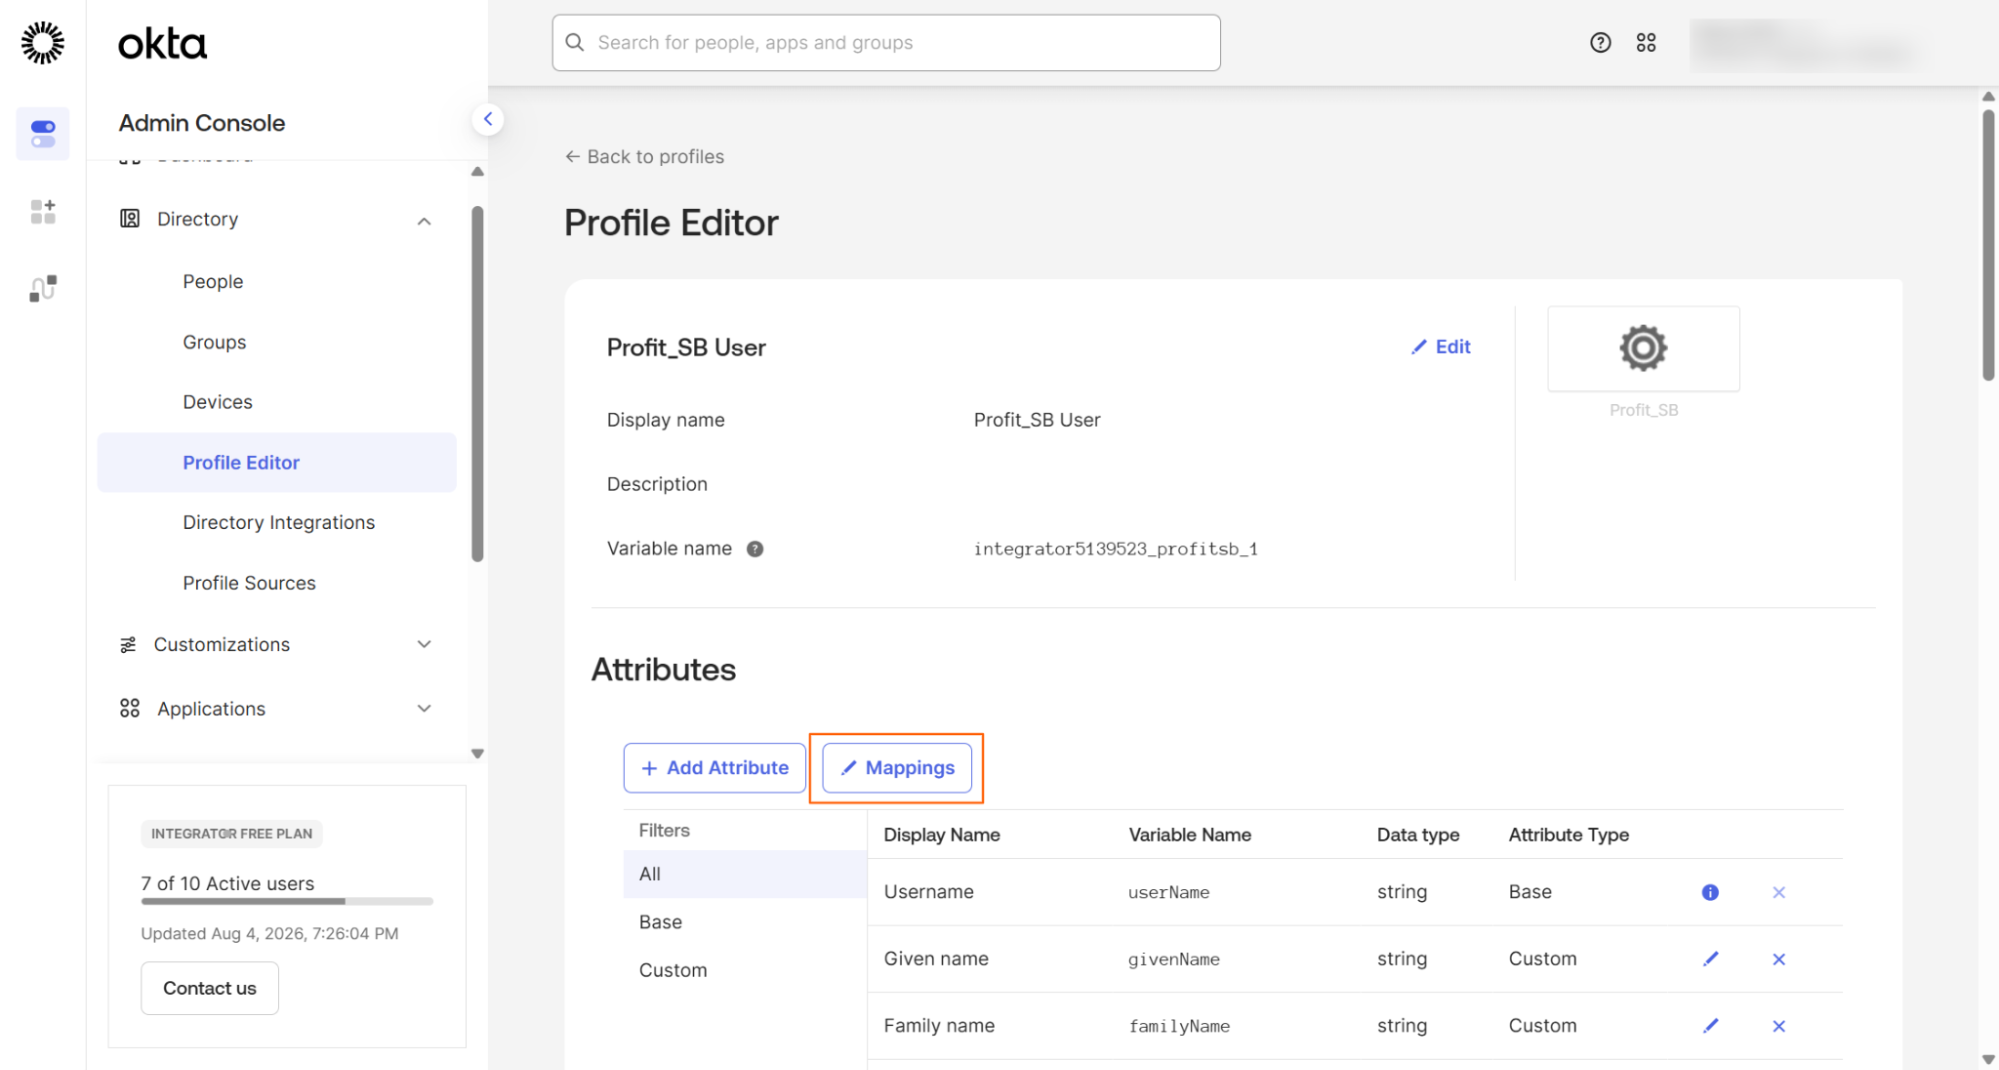
- Navigate to Directory -> Profile Editor -> Your Application -> Mappings.
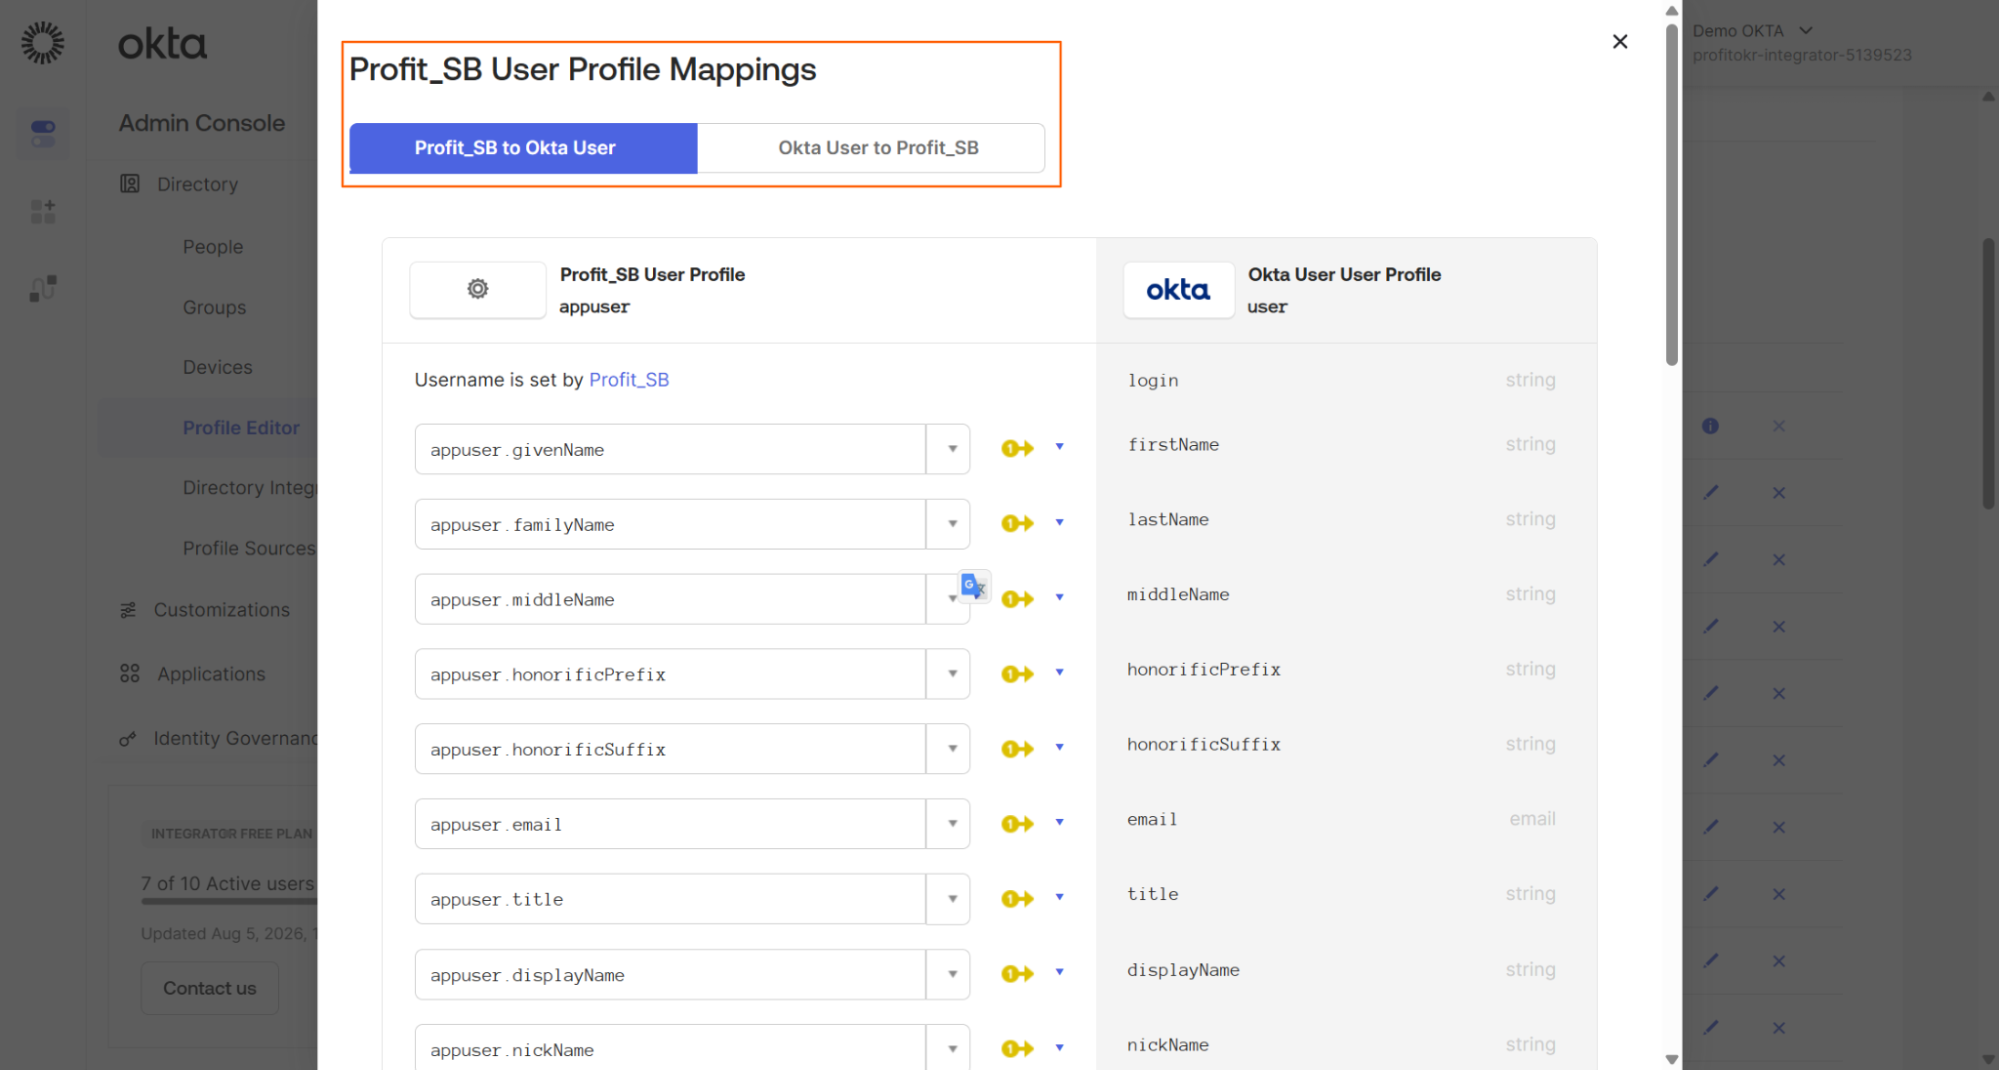
- Select the Okta User to Profit.co tab.
- Map user.role to appuser.role and click Save Mappings.
Step 3
Set the role value on individual users in Okta before they are provisioned to Profit.co.
- Navigate to Directory -> People, select the user, go to Profile, and click Edit.
- Locate the role field and enter the role (refer to the Role Sync table above).
- Click Save.
Note: If you do not configure the values above correctly, the default role will be assigned in Profit.co.
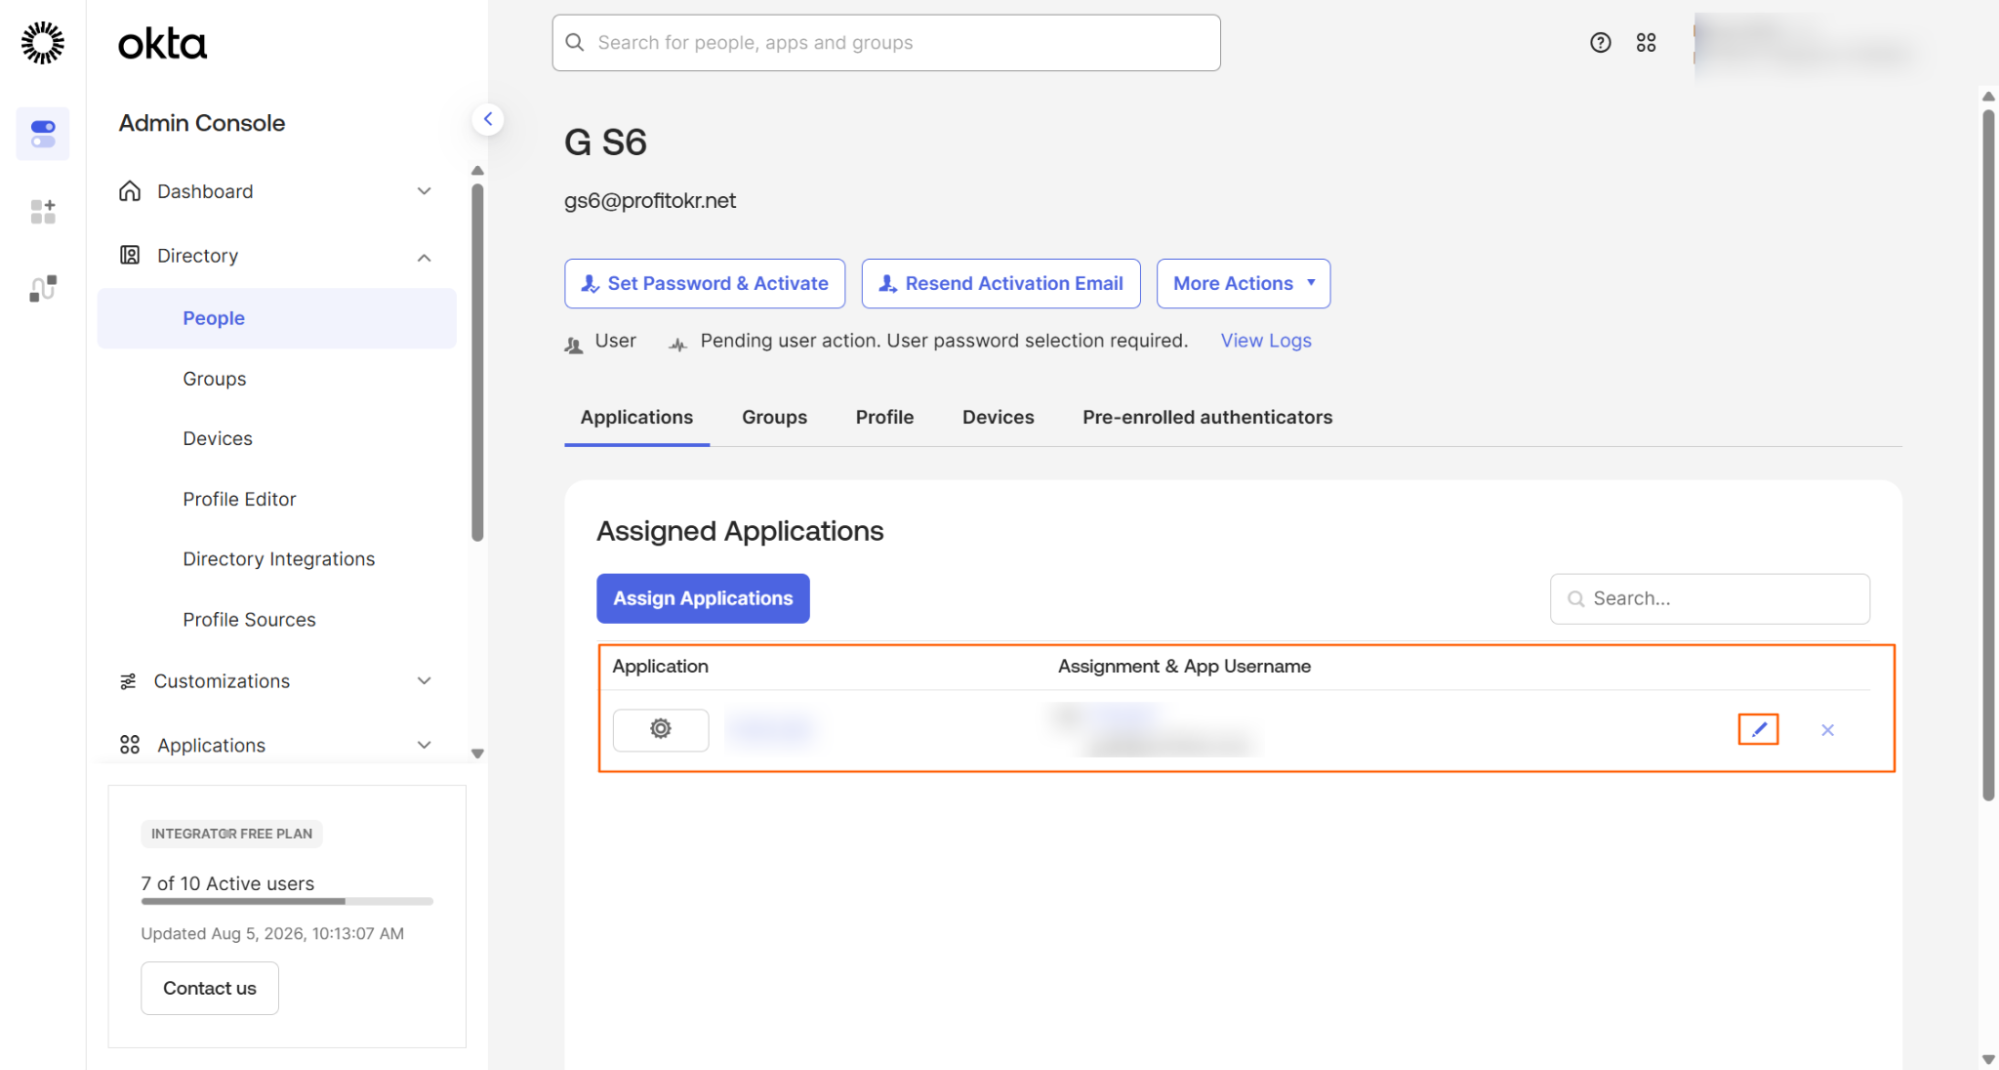
Step 4
After the user is assigned to the Profit.co app in Okta, confirm the role has been applied correctly in Profit.co.
- Navigate to Applications -> Profit.co -> Assignments in Okta and assign the user.
- In Profit.co, go to Settings -> User Management.
- Confirm the Role column reflects the value assigned in Okta.
Note: Role names are case-sensitive. The value entered in Okta must exactly match a valid role name in Profit.co for the sync to apply correctly.
Group-Based Role Assignment
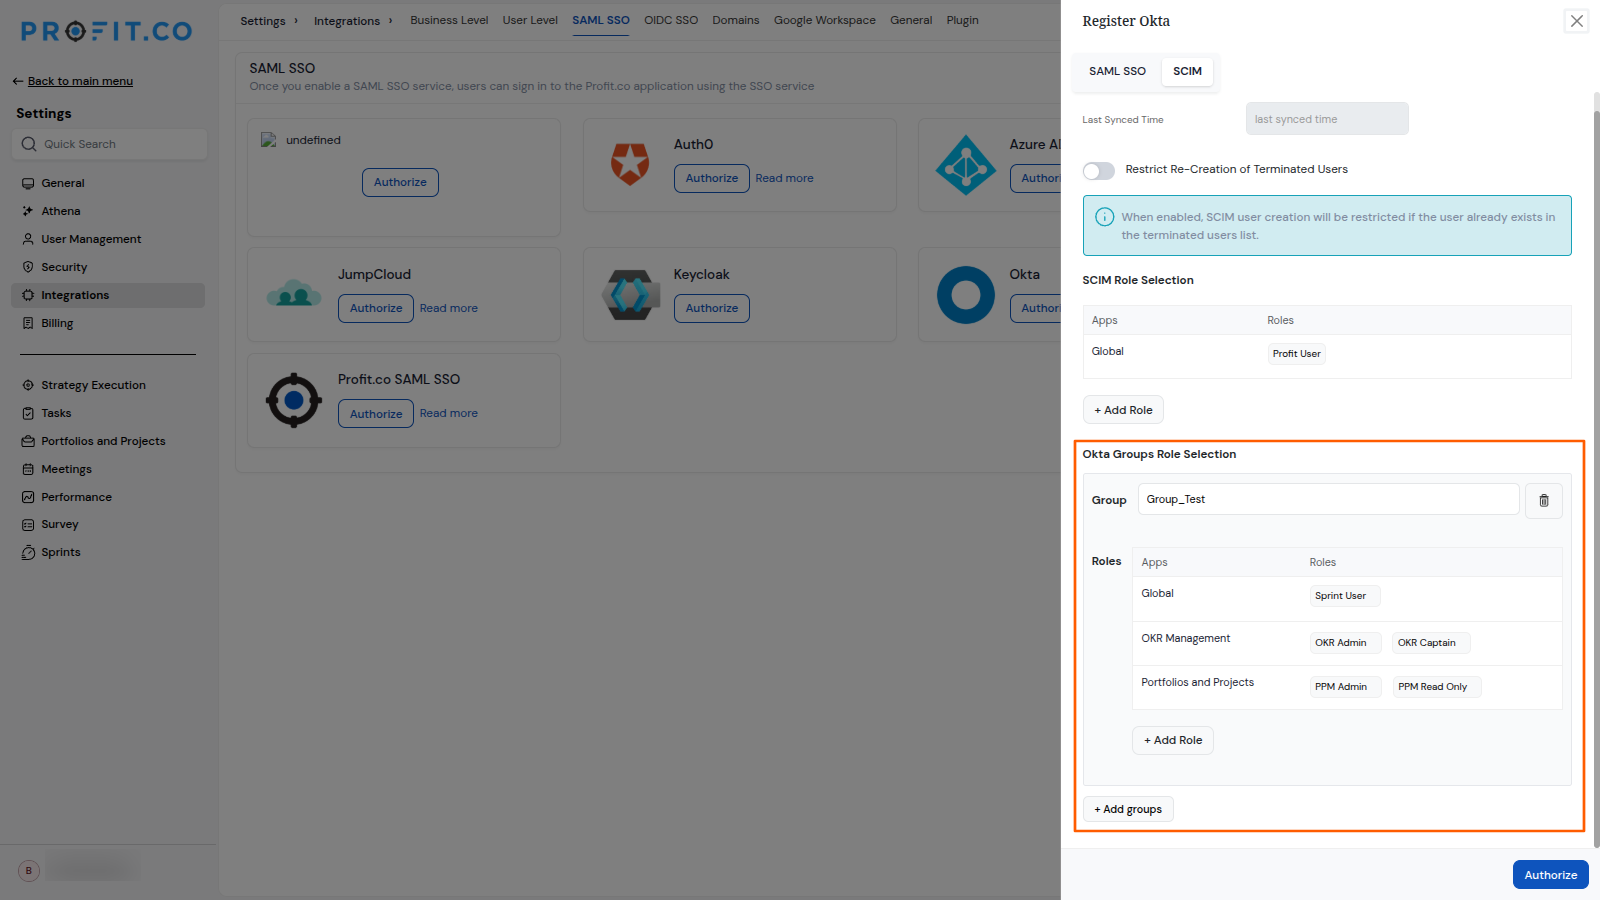
Once a group is created in Okta and users are added to it, the same group name can be configured in Profit.co for role mapping.
After this mapping is configured, whenever a user is added to the corresponding Okta group, Profit.co automatically assigns the predefined roles associated with that group.
Note: The group name must be the same as the group name in Okta SCIM for the role mapping to work.
Refer to the Group-Based SCIM Provisioning Documentation for instructions on configuring group-based user provisioning.
Troubleshooting and Support
For additional support, contact the Profit.co team at support@profit.co.
Summary
By configuring Okta as the SAML identity provider and enabling SCIM-based user provisioning, Profit.co delivers a seamless single sign-on and automated user lifecycle management experience. Employees authenticate through Okta using their existing credentials, while provisioning rules ensure that user accounts in Profit.co stay continuously aligned with your Okta directory, eliminating manual user management and maintaining secure, governed access at scale.